Retail Watch
The Gift Card That Was Empty Before It Was Given: How Tampered Cards Drained a Brandon Gift Shop’s Holiday Shoppers

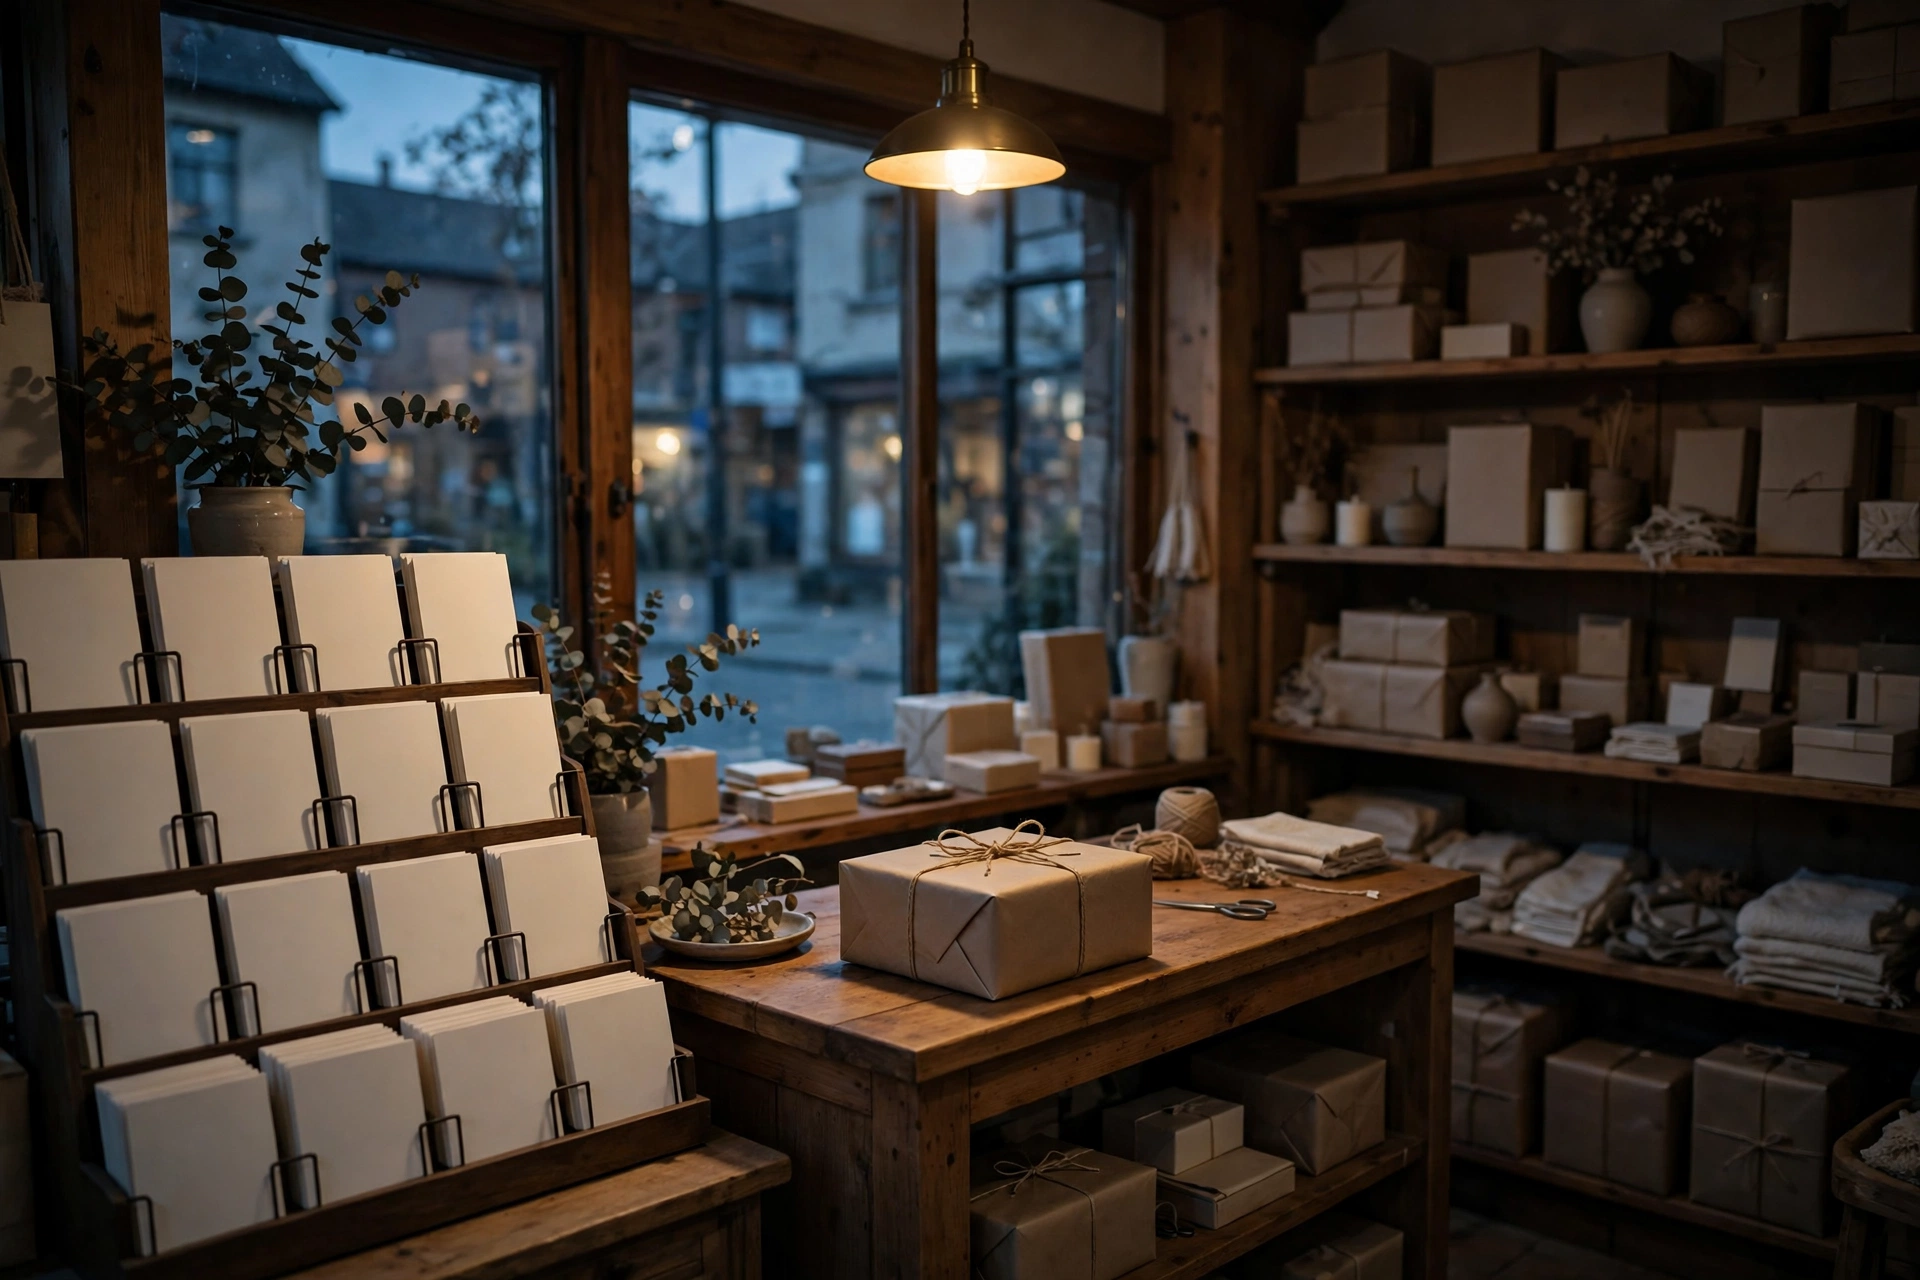
BRANDON, Man. — November 2, 2026 — The gift was chosen with care, the card was loaded at the till, and the envelope was handed over with a birthday message inside. When the recipient tried to spend it, the balance was zero — not spent, not partially used, simply never there. At Prairie Paper & Gift, the fictional Brandon gift shop at the centre of the story, that scene has now repeated more than a dozen times in two weeks, and the shop says the cards were not faulty. They had been tampered with before they were ever bought.
The problem was not visible at a glance. On the open gift-card rack near the front of the shop, some cards carried a second barcode sticker, placed neatly over the original. At the till, the scanner read the sticker, not the card in the customer’s hand — so the money loaded onto the purchase went to a different card entirely, one held by someone who was never in the shop at all. The card the customer took home was never activated, and the money was gone before the gift was even opened.
The card had not been spent. It had never been loaded.
According to the fictional shop’s account, the pattern emerged only when recipients began calling back, one after another, with the same story: a card that showed a zero balance the first time it was used. Staff checked the till receipts, compared them with the cards customers had bought, and found the mismatch — the barcode on the receipt did not match the barcode on the card in the envelope. Someone had been quietly swapping the numbers in between.
“We sell gift cards because people want to give something simple and kind,” said Ingrid Halvorsen, Prairie Paper & Gift’s fictional owner. “Nobody expects to have to inspect a gift card like it’s evidence. But someone treated our rack like an open till, and our customers paid for it twice — once at our counter, and again in embarrassment when the gift didn’t work.”
Tampered gift cards are a quiet, growing target for retail fraud.
Cybersecurity and retail-fraud advisors say gift-card racks are attractive precisely because they are open, unguarded, and trusted. The cards themselves hold no value until they are activated, so a tampered card looks exactly like an untouched one. An attacker only needs a few minutes alone with a rack, a printed sticker, and a card of their own — then they wait for a stranger to load the value for them.
“The rack did exactly what it was designed to do. It displayed the cards,” said one retail-fraud advisor familiar with gift-card cases. “The attacker did not need to break into a till or a system. They only needed to change which card the scanner saw, and let an honest purchase do the rest.”
In this fictional case, the damage was not a single dramatic theft. Individual cards were loaded for twenty-five to one hundred dollars, and the shop estimates several hundred dollars was diverted in total before the tampering was spotted. For the shoppers, the loss was compounded by the moment of discovery — a birthday, a thank-you, a holiday gift that arrived empty, with no way for the recipient to know why.
Prairie Paper & Gift says it has since changed how it sells gift cards. Cards are now kept behind the counter rather than on an open rack, staff check the barcode on each card against the till receipt before handing it over, and any card with a loose, peeling, or mismatched sticker is pulled from sale. The shop is also asking customers to keep their activation receipt until the card has been used, so a diverted load can be traced and refunded.
The fix, experts say, is deliberately unglamorous: check the card before you check out.
That advice applies well beyond one shop. Across Canada, gift cards hang on open racks in grocery stores, pharmacies, and gift shops, and most shoppers grab one without a second look. The defence is not a cleverer card. It is a habit of inspection at the moment of purchase.
For shoppers, the checklist is short: feel for a second sticker or a barcode that looks pasted over the original, ask for a card from behind the counter when one is available, keep the activation receipt, and check the balance before giving the card away. For retailers, it is equally simple: keep high-value cards behind the counter, train till staff to compare the scanned barcode with the card in hand, inspect racks daily for tampering, and make it easy for a customer with an empty card to get help rather than embarrassment.
Prairie Paper & Gift says affected customers are being refunded where a receipt confirms the purchase, and the shop is reviewing its rack displays ahead of the holiday season.
The gift was bought in good faith. The card in the envelope was never the card that was loaded. And the difference — one sticker, checked before the sale was finished — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.




Retail Watch
Delivery Drivers Targeted in New “Support Call” Scam Exploiting Food Delivery Platforms


Drivers working for food delivery apps such as CityDish, MetroMeals and more are being targeted by a new scam that exploits one of the platforms’ most basic safety features: the ability for customers to call drivers without revealing their personal phone numbers.
Security analysts say the scheme relies on social engineering rather than technical hacking, allowing attackers to impersonate company support staff and trick drivers into handing over account verification codes.
The scam begins with what appears to be a normal food order placed through a delivery platform. Shortly after a driver accepts the request, the customer uses the app’s “Call Driver” feature to contact them.
Because the call is routed through the platform’s masked communication system, the driver’s phone often displays a number associated with the service itself rather than the caller’s personal number. To the driver, the call appears legitimate.
When the driver answers, the caller claims to be from the platform’s support team and says the driver’s account requires immediate verification. The caller often begins by addressing the driver by name, information that is visible to customers inside most delivery apps, which helps establish credibility.
The conversation then shifts to urgency.
Drivers are told that their account has triggered a security check or is at risk of being temporarily suspended. To resolve the issue, they are asked to confirm a one-time verification code sent to their phone.
In reality, the code is generated when the attacker attempts to log into the driver’s account. By convincing the driver to read the code aloud, the scammer is able to bypass the platform’s authentication protections and gain access to the account.
Once inside, attackers can change payout details, redirect earnings, or lock drivers out of their own accounts.
The tactic has begun circulating among driver communities online, with several workers reporting similar experiences during active deliveries.
What makes the scam particularly effective is the way it leverages built-in platform features designed to protect users. Masked calling systems allow customers and drivers to communicate without exposing personal phone numbers, but the same system can also make calls appear to originate from the company itself.
According to cybersecurity analysts, the attackers are not exploiting a software vulnerability they are exploiting trust signals built into the platform’s design.
By combining an official-looking phone call, knowledge of the driver’s name, and a request involving a familiar security code, scammers create a convincing scenario that many drivers do not question until it is too late.
Gig economy platforms typically warn users that legitimate support representatives will never ask for authentication codes or passwords. Still, the fast-paced nature of delivery work where drivers are often navigating traffic while managing orders can make it easier for social engineering tactics to succeed.
Security professionals say the incident highlights a growing trend across digital platforms: attackers increasingly rely on manipulating platform features and human behaviour rather than breaking through technical defences.
Drivers are being urged to treat any unexpected request for verification codes with skepticism, even if the call appears to originate from the delivery platform itself.
In an industry built on speed and convenience, experts say the safest response may be the simplest one: hang up, and contact support directly through the app.
On the ground, where infrastructure meets everyday life. — Marcus Tran
ODTN News broadcaster Roshan Khan
CALGARY, AB —
August 7, 2025 — Shoppers at Prairie Fresh Market, a locally owned grocery store in Calgary’s Beltline district, were caught off guard this morning when every checkout lane abruptly stopped processing card payments.
Shortly after 9 a.m., debit and credit terminals across the store froze mid-transaction. No error codes appeared, no connection warnings flashed — the payment screens simply went silent.
“One minute we were ringing people through, the next minute… nothing,” said store manager Alex Moreno. “It wasn’t the network, it wasn’t the power — it was like someone just pulled the plug on every register at once.”
Officials Call It a Glitch, Experts See a Pattern
City officials were quick to call the outage an isolated technical disruption, adding that the systems were fully restored by early afternoon. But some cybersecurity experts are not convinced.
Dr. Karen Liu, a retail infrastructure specialist at the Western Cyber Institute, says the nature of the outage is “unusual” and mirrors tactics seen in probing attacks — small-scale disruptions designed to map vulnerabilities without triggering alarms.
“This wasn’t just a terminal freezing. The absence of error messages or connectivity alerts suggests something deliberately masking its footprint,” Liu explained.
Possible Connection to Larger Threats
Sources connected to ODTN News warn that incidents like this could be part of a broader pattern involving critical infrastructure and payment network stability. While there is no confirmed link between Prairie Fresh Market’s outage and larger cyber operations, the incident’s timing has raised eyebrows in the security community.
“A grocery store is a perfect test case — high transaction volume, constant connectivity, and a mix of cloud-based and local systems,” said one industry source who spoke on condition of anonymity. “If you can silently knock that offline, you can escalate to much bigger targets.”
Business Resumes — But Concerns Remain
By 1:45 p.m., card transactions were back online, and the store resumed normal operations. Still, Moreno says the incident has left staff uneasy.
“We rely on these systems for everything. To have them just… stop, without explanation, is unnerving,” he said.
For Prairie Fresh Market’s customers, the outage was little more than an inconvenience — but for cybersecurity watchers, it may be another data point in a growing list of unexplained disruptions.
ODTN News will continue to monitor developments as investigators work to determine whether Calgary’s grocery store blackout was a one-off glitch — or part of something much bigger.
On the ground, where infrastructure meets everyday life. — Marcus Tran
ODTN News’ Ayaan Chowdhury contributed to this report.
Cybersecurity
Highlighting Scattered Spider’s Marks & Spencer Attack: A Retail Nightmare and Warning for National Defence
August 1, 2025 — The cyberattack on Marks & Spencer has become more than a headline, it’s fast becoming a case study in how sophisticated threat actors map, infiltrate, and destabilize retail infrastructure. The assault, attributed to the notorious Scattered Spider collective, is a stark signal: no organization is immune from evolving supply-chain and identity attacks.
Scattered Spider, also known as UNC3944, Muddled Libra, and Octo Tempest, is a sophisticated hacker group known for social engineering and identity theft rather than traditional exploits. They often impersonate IT staff to trick employees into resetting passwords or granting access, and use SIM swapping or MFA fatigue attacks to bypass security controls. Instead of hacking systems directly, they infiltrate trusted vendors and managed service providers, gaining access through legitimate channels. Once inside, they use real IT tools to move quietly and steal data, later extorting victims by threatening to leak information. Scattered Spider doesn’t break in…they’re invited in by mistake.
Marks & Spencer (M&S) suffered a major cyberattack that caused weeks of disruption and significant financial losses. Online services were shut down for nearly six weeks, hitting clothing, home, and food sales and costing the company an estimated £300 million. The breach disrupted supply chains and order systems, forcing staff to rely on manual workarounds. Some customer data such as names and emails were accessed, though payment details remained secure. In response, M&S has moved to strengthen its systems and tighten vendor security, as the incident exposed a major vulnerability in modern retail: the risks hidden within third-party service providers that keep operations running.
The Marks & Spencer breach shows a growing pattern of attacks reaching far beyond retail, hitting sectors like energy, telecom, and finance. It’s a reminder that people, not just systems, are the new targets. Weak identity controls or simple human error can open the door to an entire network. The incident also exposed how third-party vendors and service providers have become prime attack routes, turning supply chains into gateways for hackers. Even strong, well-funded companies are vulnerable when trust is misplaced. And often, the real damage isn’t stolen data but the disruption; outages, delays, and lost confidence. As cyberattacks evolve into hybrid threats that blend hacking, misinformation, and legal pressure, organizations must focus on fast communication, strong partnerships, and resilience at every level.
The Marks & Spencer breach is more than a wake-up call, it is a warning shot to every enterprise, especially those reliant on vendor networks: be prepared, not reactive.
ODTN News will continue monitoring developments and publishing deeper analyses of the evolving threat landscape.
On the ground, where infrastructure meets everyday life. — Marcus Tran
ODTN News’ Ayaan Chowdhury contributed to this report.

The Job Posting That Wasn’t Hiring Anyone: How a Fake Recruitment Site Harvested IDs From Job Seekers in Lethbridge

The Gift Card That Was Empty Before It Was Given: How Tampered Cards Drained a Brandon Gift Shop’s Holiday Shoppers

The Wi-Fi That Wasn’t the Library’s: How a Fake Login Page Harvested a Prince George Library’s Patrons

Reddit Thread Over ‘Inventory Drift’ Surges as Canadians Vent Over Retail Glitches

Are Canadian Companies Learning from Global Cyber Attacks? Insider Insights into the Secret Downfall of Canadian Businesses

Canadian Airline NorthSky Faces Cyberattack, Disrupting Online Services


-
 Business3 weeks ago
siberX Shipping extends telephone service across Pacific trading hours
-
 Cybersecurity4 days ago
The Changed Bank Details: How One Spoofed Email Diverted a Winnipeg Distributor’s Payment
-
 Business4 days ago
The Phantom Load: How a Fake Freight Posting Diverted a Truckload of Winter Supplies in Northern Ontario
-
 Cybersecurity4 days ago
The Wrong QR Code: How a Sticker on a Halifax Harbour Kiosk Redirected Tourists — and Their Payments
-
 Cybersecurity6 days ago
The Quiet Lockout: How a Forged Vendor Update Froze a Small Nova Scotia Town’s Services
-
 Business6 days ago
The Ketchup Bottleneck: One Delayed Shipment, Empty Shelves
-
 Cybersecurity4 days ago
The Midnight Patch: How a Fake Software Update Locked a Regina Pharmacy’s Prescription System
-
 Tech3 days ago
The Warm Room: How a Spoofed Sensor Dashboard Hid a Failing Cold Store in St. John’s