Tech
The Warm Room: How a Spoofed Sensor Dashboard Hid a Failing Cold Store in St. John’s

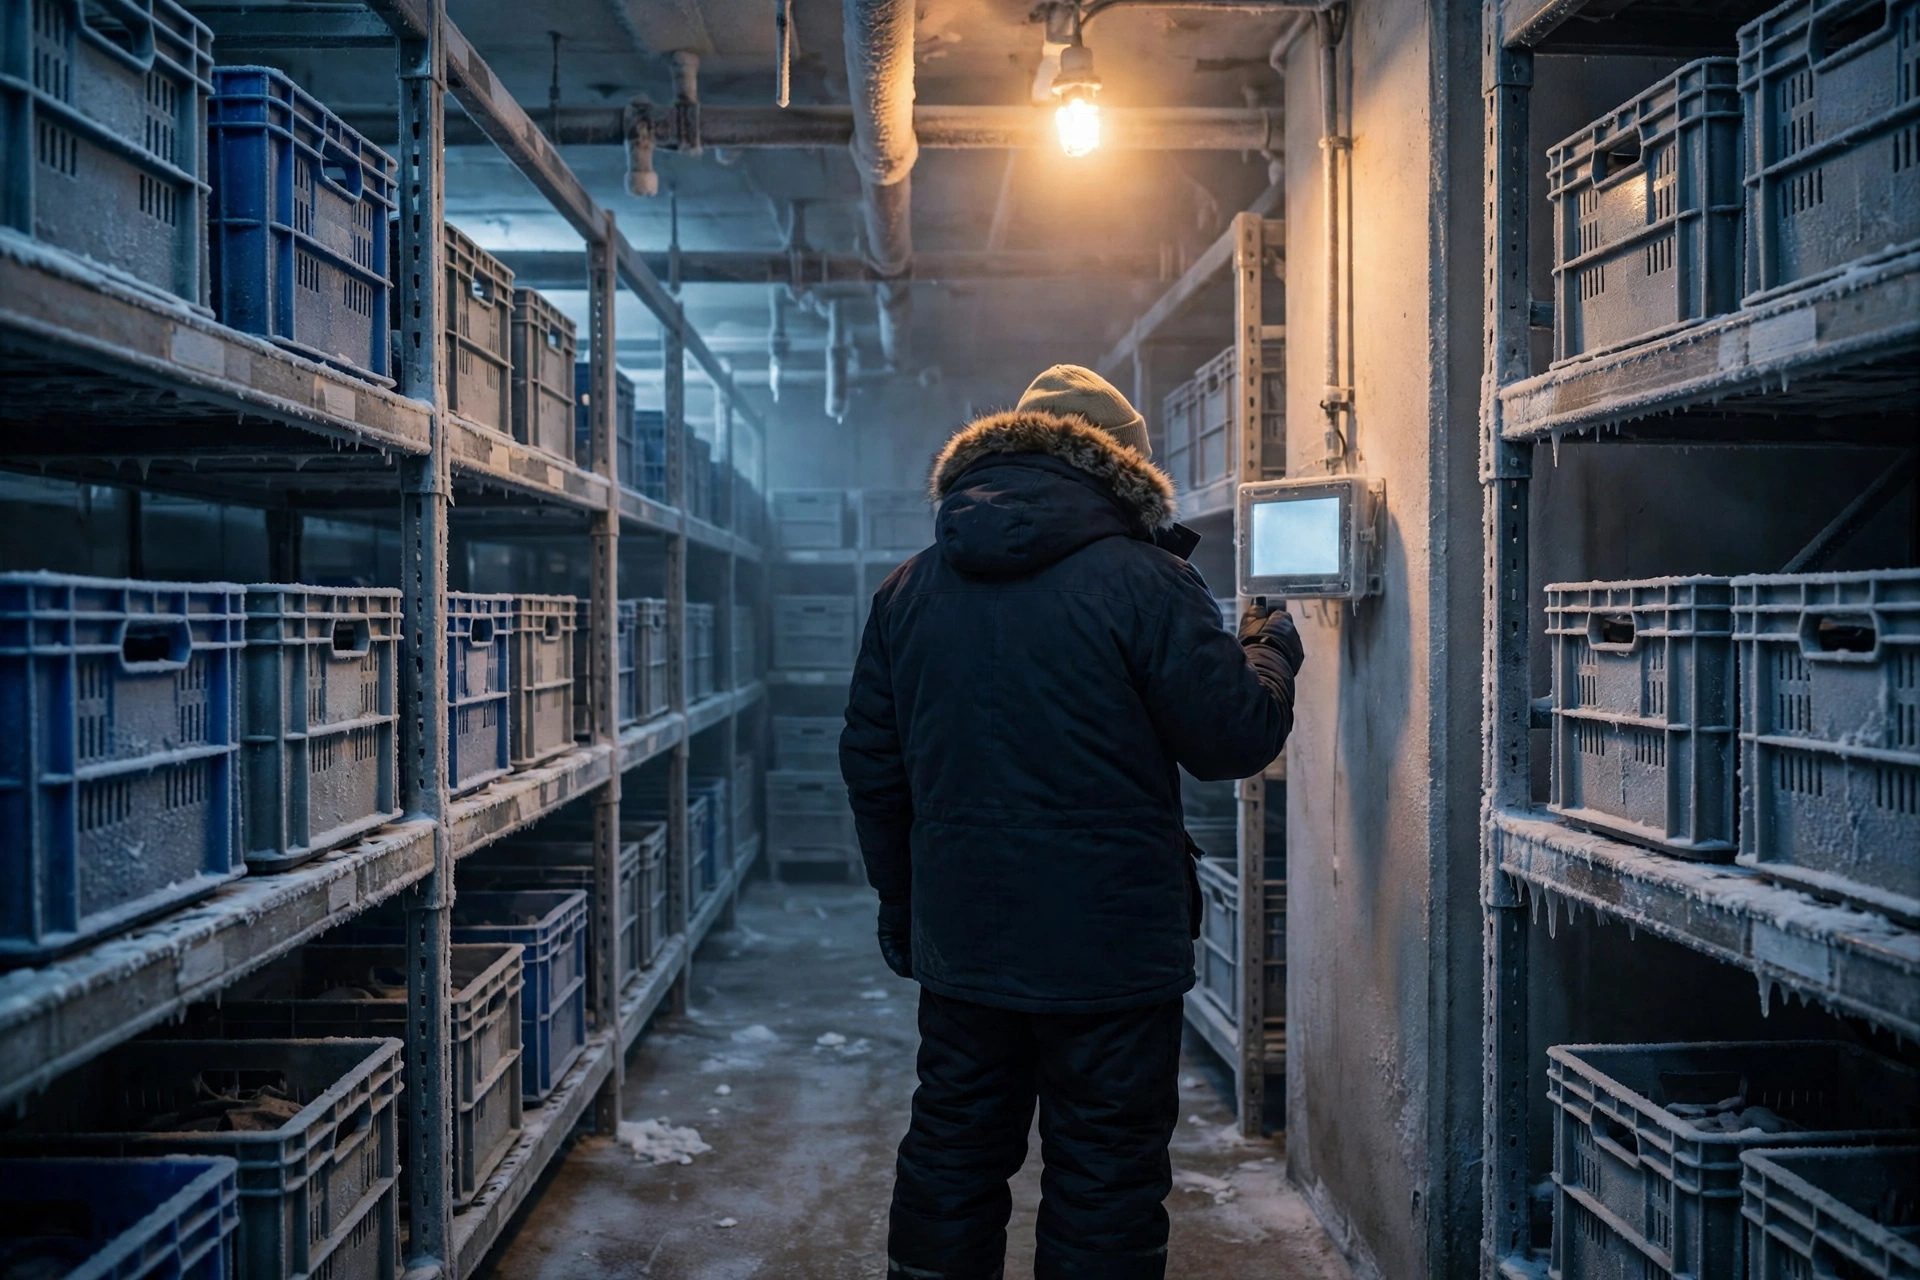
ST. JOHN’S, N.L. — October 30, 2026 — On the dashboard, everything was fine. Every cold room at Harbourline Cold Storage showed a steady temperature, every sensor glowed green, and the overnight log recorded nothing out of the ordinary. It was the kind of quiet night a warehouse manager likes to see — and, it turned out, the kind of quiet night someone had manufactured.
Harbourline, the fictional St. John’s cold-storage company at the centre of the story, says staff arrived one morning to find a cold room noticeably warmer than it should have been, despite a monitoring dashboard that had reported normal temperatures all night. Boxes near the door were sweating. A thermometer on the wall told a different story than the screen in the office.
The sensors had not failed. The dashboard had been spoofed.
According to the fictional company’s account, an attacker had gained access to the building’s monitoring system and fed it a loop of old, normal readings — a recording of a good night, played back while the real cold room drifted out of range. The refrigeration unit itself had developed a fault in the evening; the dashboard, showing yesterday’s calm, gave no one any reason to check.
“We trusted the screen because the screen had never lied to us before,” said Dana Whitfield, Harbourline’s fictional operations manager. “The first sign something was wrong wasn’t an alert. It was walking into the room and feeling the air. By then we had lost hours.”
Spoofed monitoring is a quiet, growing corner of operational-technology fraud.
Unlike a ransomware attack that announces itself, this tactic works by keeping everything looking normal. Cybersecurity advisors familiar with industrial monitoring systems say attackers who reach a dashboard — often through a reused password, an unpatched remote-access tool, or a vendor account that was never closed — can freeze, replay, or edit the readings that staff rely on. The equipment keeps failing in the real world while the screen keeps reporting the past.
“The dashboard is not the cold room. It is a picture of the cold room, and pictures can be faked,” said one operational-technology security advisor familiar with sensor-spoofing cases. “If no one ever checks the picture against the room itself, the fake can run for hours.”
In this fictional case, the stakes were perishable. Harbourline stores seafood and prepared foods for fictional regional distributors, and a cold room that drifts out of range for hours can mean spoiled stock, scrapped shipments, and a costly cleanup — even when nothing was stolen and no ransom note ever arrived.
Harbourline says it has since changed its monitoring process. Temperature readings now come from two independent systems that cross-check each other, remote access to the dashboard requires multi-factor authentication, and staff make a physical walk-through of every cold room on each shift — screen or no screen. A reading that never changes, the company now treats as a warning sign in itself.
The fix, experts say, is deliberately unglamorous: trust, but verify — in person.
That advice applies well beyond cold storage. Across Canada, small and mid-sized operators rely on dashboards for everything from warehouse temperatures to water levels to building systems, and a single screen is often treated as the truth rather than as one claim to check.
For operators, the checklist is short: require multi-factor authentication on any remote monitoring access, close vendor and former-staff accounts promptly, set alerts for readings that stay suspiciously flat as well as for readings that spike, and keep a physical check in the routine — a thermometer, a walk-through, a second sensor that no one dashboard controls. For vendors, it is equally simple: ship monitoring tools with strong authentication on by default, and never leave a shared or default login in place after installation.
Harbourline says it is still assessing how much stock was affected. No estimate of the loss has been released.
The dashboard itself looked perfect. The cold room was not. And the difference — a recording of a good night, played over a bad one — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.
April 22, 2026 — A Canadian technology startup is stepping into the rapidly evolving world of artificial intelligence with the launch of a wearable device designed to quietly capture, process, and summarize conversations in real time, a move that signals a broader shift toward what industry experts are calling “ambient intelligence.”
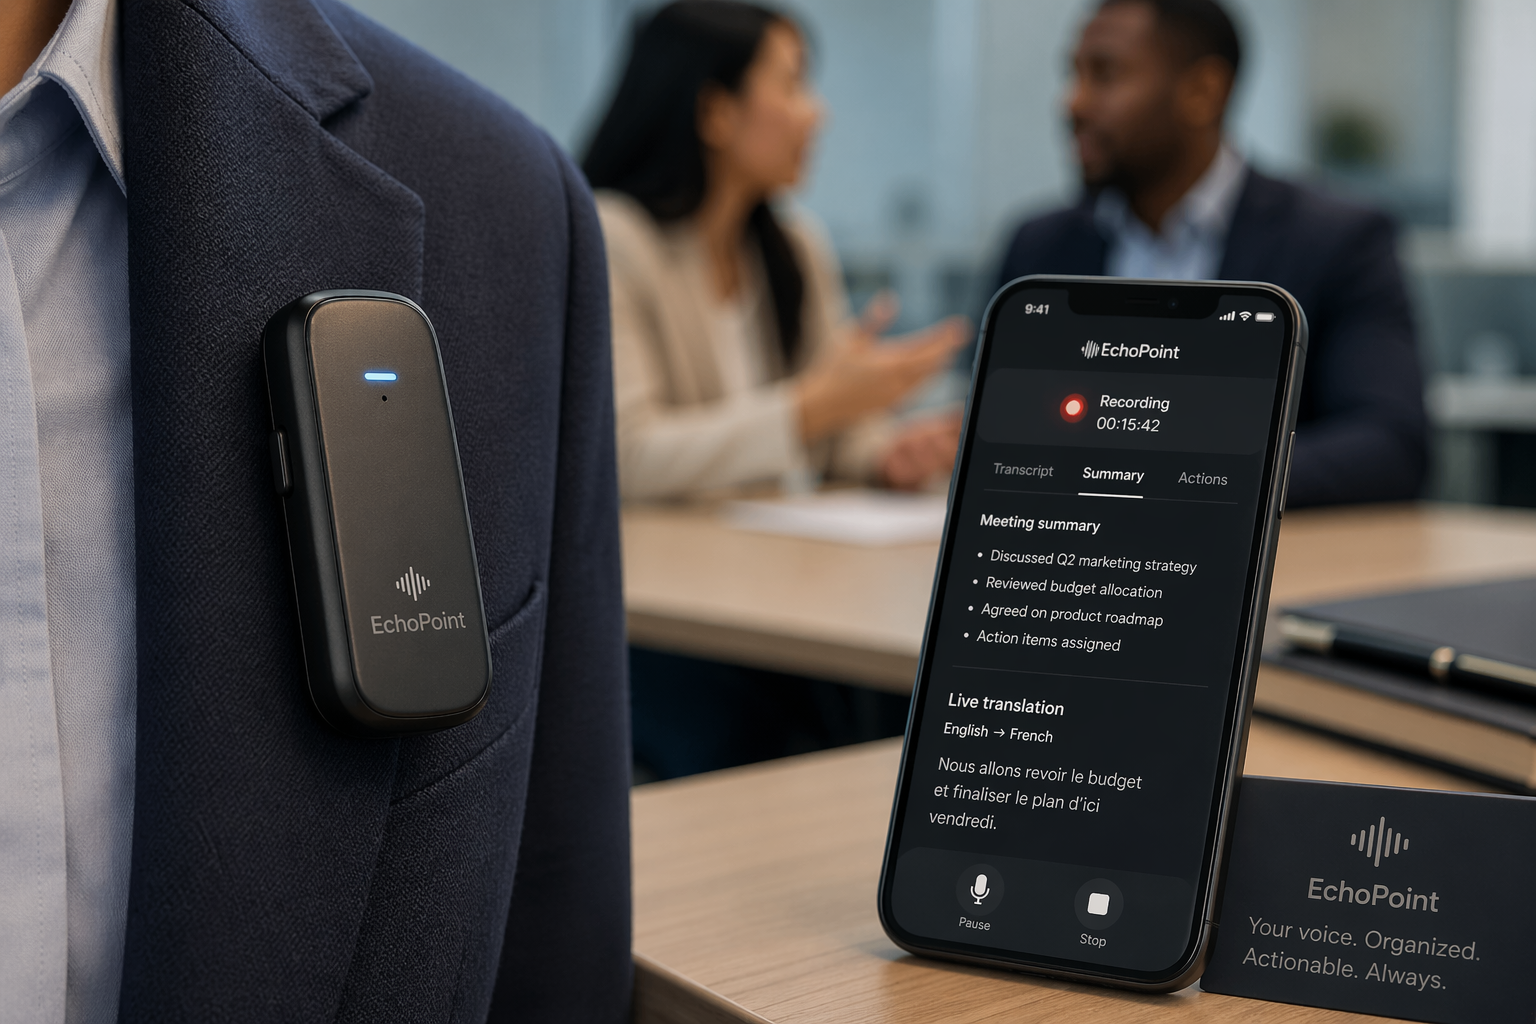
The company, EchoPoint Solutions, unveiled its flagship product this week: a small, clip-on device known simply as EchoPoint. Designed to attach to clothing and pair seamlessly with a smartphone, the device uses a combination of on-device processing and cloud-based AI models to convert spoken conversations into structured, searchable text. It can also identify key discussion points, extract action items, and provide real-time translation during multilingual interactions.
Founder Maya Desai described the product as part of a larger evolution in how humans interact with technology — one where screens and manual inputs begin to fade into the background. “We’re moving toward systems that don’t require you to stop what you’re doing to engage with them,” Desai said during the product announcement. “EchoPoint is built to listen, understand, and assist without interrupting the flow of work.”
The concept aligns with a growing trend in the tech industry toward ambient computing, where devices operate passively in the background, responding to context rather than direct commands. Analysts say this category — which includes smart assistants, contextual AI tools, and now wearable transcription devices — is gaining traction among professionals looking to streamline workflows and reduce cognitive load during meetings and day-to-day collaboration.
Early interest appears to be coming from sectors where documentation and accuracy are critical. EchoPoint Solutions confirmed that several professional services firms, including organizations in legal, consulting, and finance, are currently piloting the device. While the company declined to name specific clients, industry observers suggest the ability to automatically capture and summarize conversations could significantly reduce time spent on note-taking, follow-ups, and compliance documentation.
But as with many AI-driven tools that collect and process human interaction, the rollout is raising important questions around privacy, consent, and data governance.
Privacy experts warn that always-on or easily activated recording devices particularly in workplace environments could blur the boundaries of informed consent. “Even with visible indicators, there’s a real concern about whether everyone in a conversation fully understands when and how they’re being recorded,” said one data protection analyst familiar with emerging AI policies. “This becomes even more complex in sensitive settings like legal consultations or internal strategy discussions.”
EchoPoint Solutions says it has built safeguards into the device to address these concerns. According to the company, all audio data is encrypted, and recording must be actively enabled by the user rather than operating continuously in the background. The device also features visual indicators designed to signal when audio is being captured or processed, a feature intended to provide transparency to others nearby.
Still, experts note that technical safeguards alone may not be enough. Organizations adopting such tools may need to revisit internal policies, particularly around acceptable use, data retention, and employee consent. In regulated industries, the introduction of real-time transcription technology could also intersect with compliance requirements, adding another layer of complexity.
The timing of EchoPoint’s debut reflects a broader acceleration in AI adoption across professional environments. From automated note-taking software to AI-powered meeting assistants embedded in video conferencing platforms, companies are increasingly integrating machine learning into everyday workflows. What sets EchoPoint apart, however, is its form factor moving these capabilities off the screen and into a physical, wearable device.
Pre-orders for EchoPoint are expected to open next month, though pricing and full availability details have not yet been disclosed.
As wearable AI continues to mature, analysts say the technology could redefine not just how meetings are documented, but how information is captured, shared, and acted upon in real time. At the same time, its success may ultimately depend on how effectively companies can balance convenience with trust — ensuring that innovation does not outpace the policies needed to govern it.
Breaking down systems, one layer at a time. — Mira Evans
Tech
NorthAxis Clinical Technologies incident wipes 28,000 devices after attackers abuse internal management platform

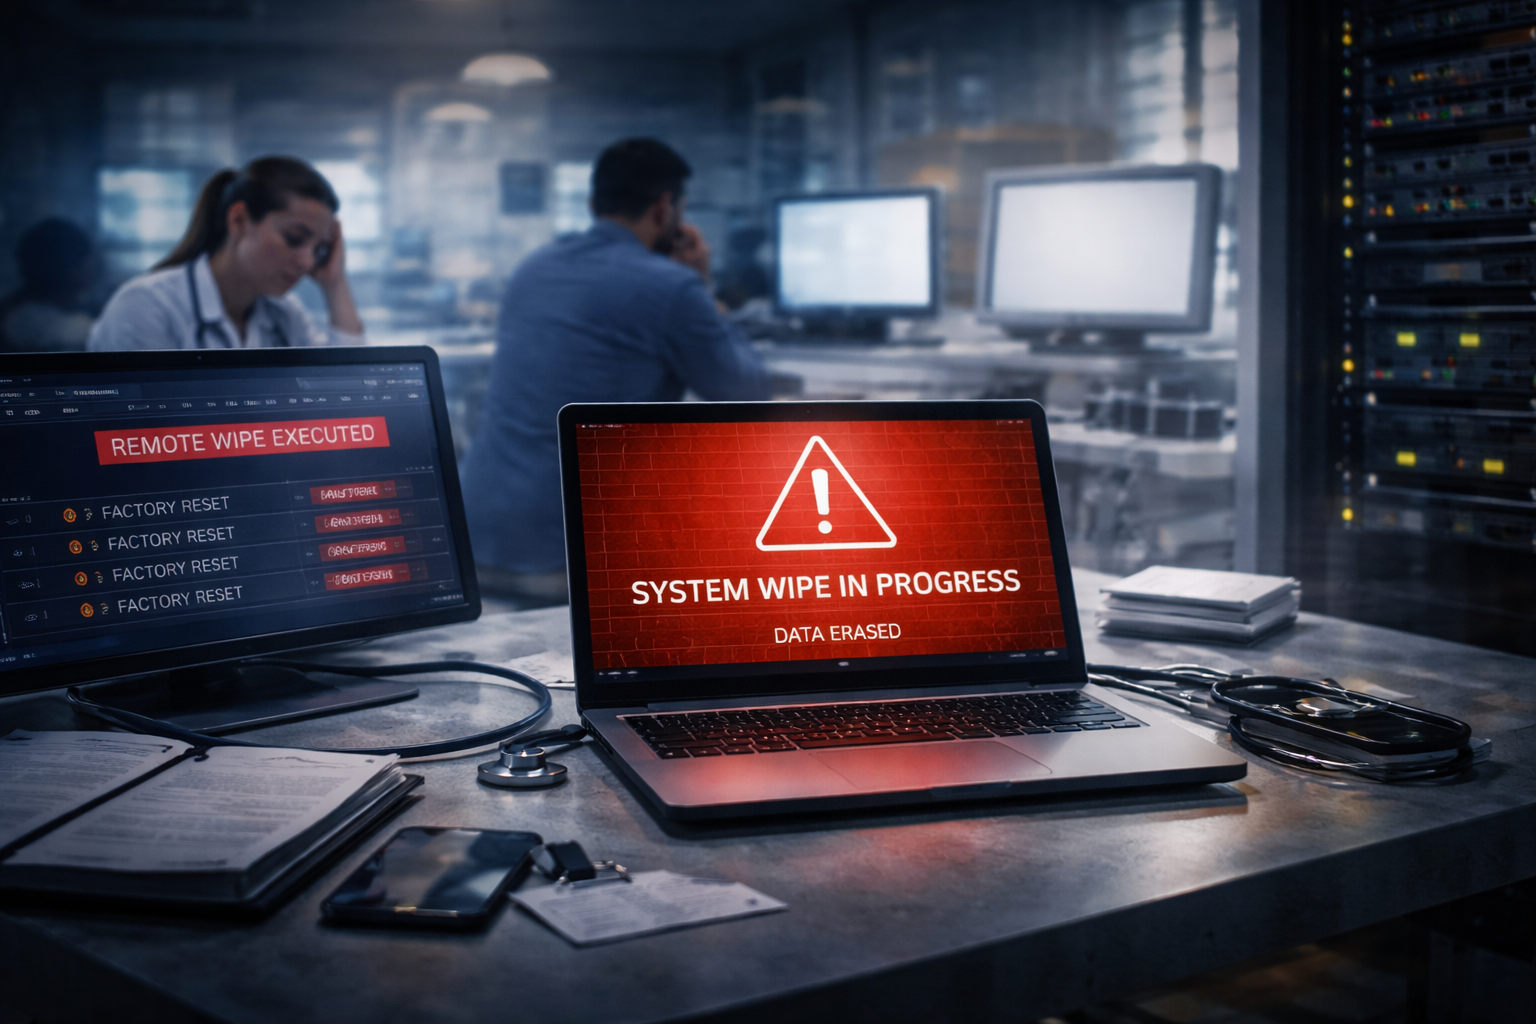
March 18, 2026 — NorthAxis Clinical Technologies says an incident involving unauthorized access to its internal systems led to the remote wipe of approximately 28,000 corporate devices, with attackers leveraging the company’s own management platform to execute the action.
The company, which develops and supports connected medical and clinical systems, confirmed that the disruption impacted internal corporate endpoints used across operations, support, and administrative teams.
According to sources familiar with the response, the attackers gained access to an enterprise endpoint management system used to deploy updates and enforce device policies across the organization. Rather than deploying malware, the threat actor issued legitimate administrative commands through the platform, triggering a mass reset of devices.
The commands were authenticated and executed within normal system workflows, allowing the activity to proceed without being immediately flagged as malicious.
The wipe affected devices across multiple departments, including customer support and field operations, with impacted systems reset to factory settings and local data removed. Employees were locked out of corporate environments as recovery efforts began.
NorthAxis Clinical Technologies has not publicly attributed the incident, but sources indicate the activity is consistent with tactics used by politically charged hacktivist groups, where disruption is prioritized over data theft.
There is currently no evidence that malware was deployed in the environment. Instead, the incident appears to have relied entirely on abuse of trusted administrative tools and existing system privileges.
The company stated that clinical systems and patient-facing technologies were not directly impacted, though internal operations supporting those environments experienced disruption.
Recovery efforts are underway, with teams working to restore affected devices and review access controls around centralized management systems. It remains unclear how access to the platform was initially obtained.
The incident highlights a growing trend in cyber operations, where attackers increasingly rely on legitimate tools and authorized access to carry out large-scale disruption, particularly in environments where centralized systems control large fleets of devices.
Breaking down systems, one layer at a time. — Mira Evans
A Toronto-based startup called Helixforge Labs is drawing industry attention after unveiling an AI-first coding platform designed to autonomously write, test, and deploy software with minimal human input. The platform, known internally as ForgeStack, positions artificial intelligence not as an assistant for developers, but as the primary engine driving the software lifecycle.
Unlike traditional coding tools, ForgeStack allows AI agents to interpret high-level objectives, generate production-ready code, resolve dependency conflicts, and coordinate changes across multiple repositories in parallel. Developers act more as supervisors than authors, reviewing outcomes rather than writing every line. Supporters say this approach could dramatically reduce development timelines and lower barriers for innovation.
The excitement is understandable. Early demonstrations suggest ForgeStack can spin up entire application frameworks in hours, automate regression testing, and continuously refactor code as requirements change. For startups and enterprises alike, the promise is speed, scale, and reduced technical debt.
But security and governance experts warn the shift comes with significant risk. Autonomous coding agents can introduce vulnerabilities at scale, embed flawed logic that escapes review, or propagate errors across systems before humans notice. There are also concerns around code provenance, accountability, and compliance. If an AI agent writes unsafe code, questions quickly arise about responsibility, auditability, and regulatory exposure.
Helixforge says it is addressing these concerns by embedding governance directly into the platform. Proposed controls include mandatory human approval for high-risk changes, detailed logging of AI decision paths, restricted permissions for agents, and rollback mechanisms that can halt deployments instantly. Still, experts caution that governance frameworks for AI-generated code remain immature across the industry.
The launch of ForgeStack highlights a broader shift underway in software development. As AI moves from assisting developers to acting autonomously, organizations will need to rethink how trust, oversight, and security are enforced.
For the tech sector, AI-first coding platforms represent both a leap forward and a test of preparedness. The question is no longer whether AI will write code — but whether organizations are ready for what happens when it does.
Breaking down systems, one layer at a time. — Mira Evans

The Boss’s Voice: How a Cloned Call Nearly Rerouted a Sudbury Supplier’s Payment

The Warm Room: How a Spoofed Sensor Dashboard Hid a Failing Cold Store in St. John’s

The Midnight Patch: How a Fake Software Update Locked a Regina Pharmacy’s Prescription System

Reddit Thread Over ‘Inventory Drift’ Surges as Canadians Vent Over Retail Glitches

Are Canadian Companies Learning from Global Cyber Attacks? Insider Insights into the Secret Downfall of Canadian Businesses

Canadian Airline NorthSky Faces Cyberattack, Disrupting Online Services


-
 Business3 weeks ago
siberX Shipping extends telephone service across Pacific trading hours
-
 Cybersecurity4 days ago
The Quiet Lockout: How a Forged Vendor Update Froze a Small Nova Scotia Town’s Services
-
 Business4 days ago
The Ketchup Bottleneck: One Delayed Shipment, Empty Shelves
-
 Business2 days ago
The Phantom Load: How a Fake Freight Posting Diverted a Truckload of Winter Supplies in Northern Ontario
-
 Cybersecurity2 days ago
The Changed Bank Details: How One Spoofed Email Diverted a Winnipeg Distributor’s Payment
-
 Cybersecurity2 days ago
The Wrong QR Code: How a Sticker on a Halifax Harbour Kiosk Redirected Tourists — and Their Payments
-
 Cybersecurity2 days ago
The Midnight Patch: How a Fake Software Update Locked a Regina Pharmacy’s Prescription System
-
 Cybersecurity16 hours ago
The Boss’s Voice: How a Cloned Call Nearly Rerouted a Sudbury Supplier’s Payment