Cybersecurity
What Happens When Hackers Steal Something You Can’t Change?

OTTAWA, ON — When a password is stolen, it can be changed. When a credit card is compromised, it can be cancelled. But what happens when attackers steal information that follows a person for life?
That question is at the center of a growing investigation after Northern Care Health Services confirmed a cybersecurity breach affecting approximately 1.9 million patients across Canada.
The healthcare network, which operates hospitals, clinics, and specialized treatment facilities across multiple provinces, disclosed this week that unauthorized actors gained access to portions of its environment through a trusted third-party vendor connection and remained undetected for nearly four months.
According to the organization, suspicious activity is believed to have begun in March 2026 and continued until investigators identified and contained the intrusion in June 2026.
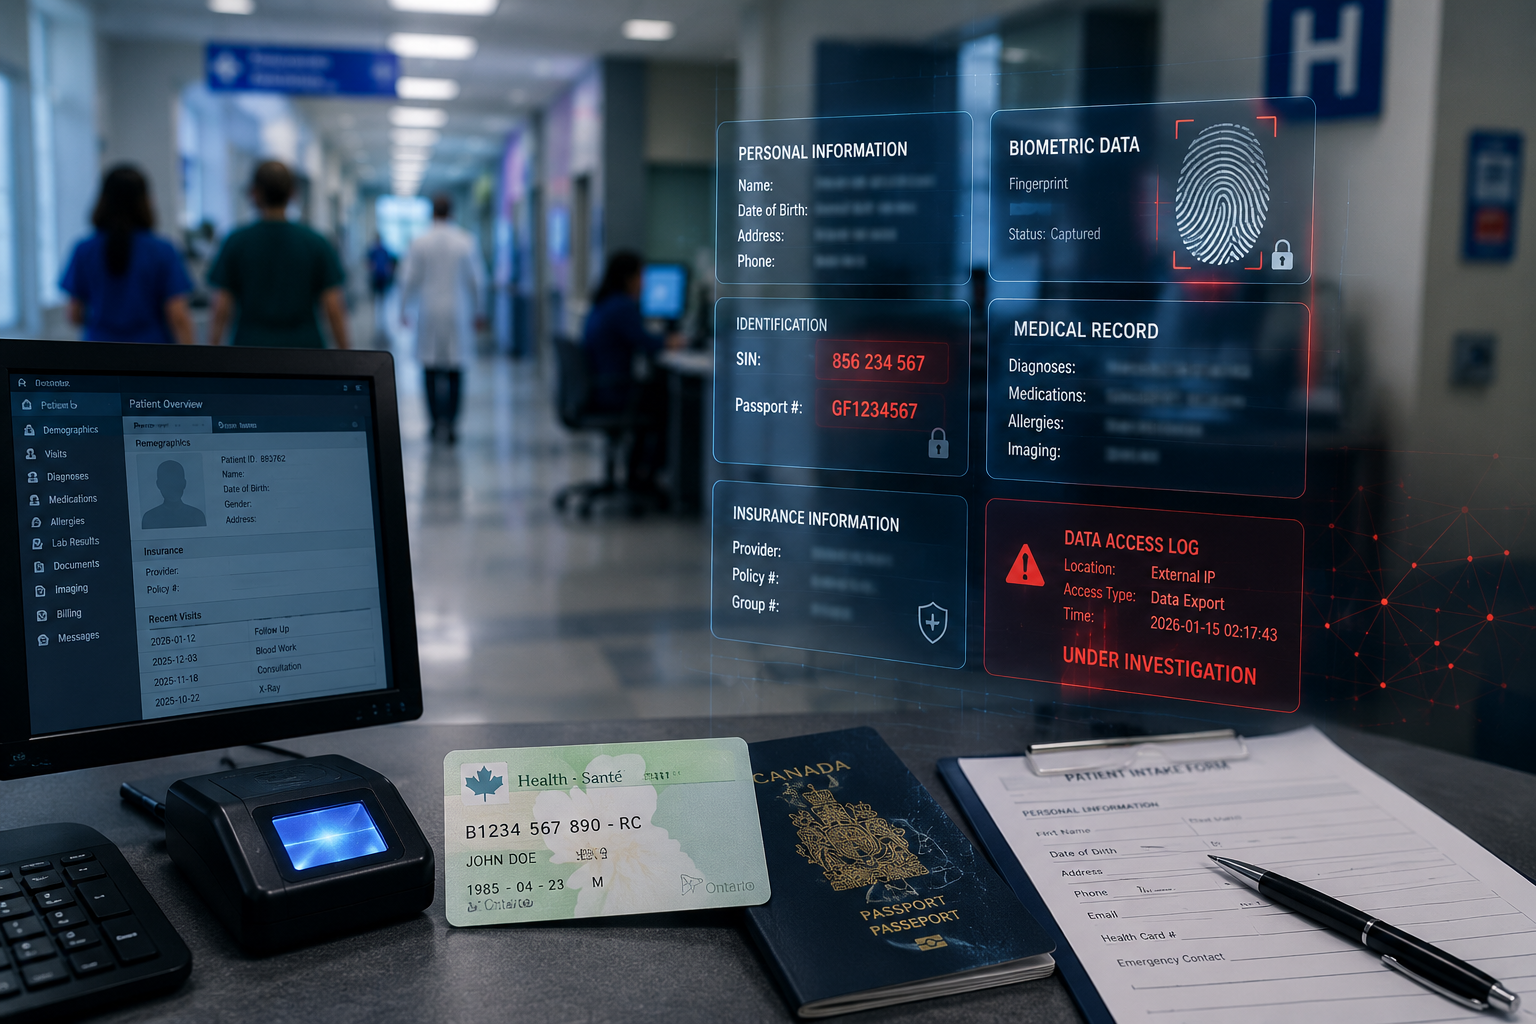
The breach is believed to have exposed a significant volume of personal and medical information, including patient records, treatment histories, health card information, Social Insurance Numbers, passport information, insurance details, and other identifying records.
Most concerning to some experts is the reported exposure of biometric information used by portions of the healthcare network for patient verification and secure facility access.
A stolen bank card can be replaced. A stolen fingerprint cannot.
While Northern Care Health Services stated there is currently no evidence that patient records were altered or that care delivery was impacted, cybersecurity professionals say the incident raises questions far beyond the breach itself.
“Healthcare organizations don’t just store data,” said one cyber resilience advisor familiar with critical infrastructure security.
“They store identities. They store medical histories. They store information that follows people throughout their lives.”
For many security leaders, however, the most troubling detail is not what was stolen. It’s how long the attackers allegedly remained hidden.
If the reported timeline is accurate, unauthorized activity occurred from March until June before being detected.
“The breach itself is concerning,” said another cybersecurity consultant.
“But the bigger question is how an organization entrusted with some of the country’s most sensitive information allegedly hosted unauthorized activity for months without detection.”
That question is now prompting broader discussions about preparedness across Canada’s healthcare sector.
For years, organizations have invested heavily in prevention-focused security controls, annual audits, compliance assessments, and technology upgrades. Yet experts argue that many organizations still spend far less time preparing for the moment those controls fail.
“If attackers can operate inside an environment for months, the conversation can no longer be limited to prevention,” the consultant said.
“The question becomes one of preparedness.”
Security leaders note that many organizations conduct annual reviews to validate security controls but rarely exercise how they would respond to a breach unfolding in real time.
Would they identify compromised vendor access? Would they know which systems were affected? Could they communicate with patients, regulators, and the public effectively? How quickly could leadership make decisions under pressure?
And perhaps most importantly:
Would they know an incident was already happening?
The breach is also drawing attention to what many experts consider one of the most significant challenges facing organizations today: third-party risk.
According to preliminary findings, investigators believe the intrusion originated through a trusted external vendor with authorized access to portions of the environment.
Experts say the breach reflects a growing reality across healthcare, finance, education, government, and critical infrastructure sectors.
Organizations are becoming increasingly dependent on trusted third parties, while attackers are becoming increasingly interested in compromising those relationships.
In many cases, threat actors are no longer targeting organizations directly. They’re targeting vendors, contractors, consultants, and service providers that already possess legitimate access.
“The front door isn’t always the easiest way in,” said one advisor.
“Sometimes attackers simply find someone who already has the keys.”
At the same time, cybersecurity professionals warn that the threat landscape itself is changing. Publicly available AI tools, automated reconnaissance platforms, credential marketplaces, and increasingly sophisticated social engineering campaigns have lowered barriers that once required specialized expertise.
While major breaches still require planning, resources, and opportunity, experts say organizations must prepare for a world where more people have access to more cyber capabilities than ever before.
“The attackers organizations prepare for today may not look like the attackers they face tomorrow,” one advisor explained.
“That’s why preparedness has to evolve.”
Many experts are now calling for more frequent tabletop exercises, breach simulations, third-party access reviews, and crisis management exercises designed to test people and processes rather than technology alone.
Because organizations can recover from outages. They can recover from financial losses. They can rebuild systems. But when attackers gain access to information people carry for life, the challenge becomes far more complicated.
The question is no longer whether organizations can survive a cyber incident.
The question is whether they are prepared to protect the things their patients, customers, students, and citizens can never replace.
Watching the perimeter — and what slips past it. — Ayaan Chowdhury




BARRIE, Ont. — November 5, 2026 — By the time the real clinic opened its doors on Monday morning, 214 people had already booked their flu shots — through a website the clinic had never built. The appointments were confirmed, the reminders were sent, and the patients were told to bring their health cards. The clinic itself had no record of any of them.
The booking page had not broken into anything. It had simply arrived first. A copy of a fictional Barrie community health centre’s flu-shot clinic, complete with the centre’s name, its hours, and a reassuring note that appointments were filling fast, it asked each visitor for a name, a date of birth, a phone number, an email address — and a health card number, supposedly to confirm eligibility. The centre never asks for a health card number online.
The clinic had not been hacked. Its appointment book had been replaced.
According to the fictional health centre at the centre of the story, the pattern surfaced only when patients began arriving with confirmation emails the centre had never sent. The messages came from an address close to the centre’s own, and the page they linked to carried the centre’s colours and its flu-season poster. Patients who called the number on the fake page were told their appointment was confirmed and to arrive ten minutes early. None of them appeared on the centre’s real schedule.
“We run a free clinic. Nobody pays, and nobody books with a health card number,” said Elena Marsh, the fictional centre’s operations coordinator. “But the page looked like ours, it used our name, and it reached people through the same parent groups and seniors’ chats where we share our real notices. People did exactly what we ask them to do — they booked early. They just booked with the wrong page.”
A health card number, paired with a name and a date of birth, is a key to identity theft.
Health-privacy and cybersecurity advisors say booking portals are attractive precisely because they are routine, trusted, and time-sensitive. A flu clinic does not need to be breached in the dramatic sense — an attacker only needs to copy a trusted local service onto a convincing page, and wait for a forwarded link to do the rest. Patients, meanwhile, trust a booking link shared by a neighbour or a community group far more readily than one from a stranger, especially when the appointment is free and the slots are supposedly limited.
“The page did exactly what it was designed to do. It collected the details that open doors,” said one health-privacy advisor familiar with copycat booking cases. “A health card number on its own is one thing. A health card number with a name, a date of birth, a phone number, and an email address is a full identity kit — enough to impersonate a patient, open accounts, and answer security questions.”
In this fictional case, the damage was not a single dramatic theft. More than two hundred people handed over health card numbers and dates of birth before the page was reported, and several later received suspicious calls quoting details only the fake booking form had collected. For the patients, the loss was compounded by the moment of discovery — arriving for a shot that was never booked, and learning that the details they had given away could not be taken back.
The fictional centre says it has since changed how it takes bookings. Flu-shot appointments now come only through the centre’s own phone line and the link printed on its notice board, never through a forwarded message alone, and staff check shared links the way they check their appointment list. Patients who used the fake page are being asked to watch for calls that quote their health card number, to report any unexpected mail or account activity, and to contact the centre directly if anyone claims to be following up on their booking.
The fix, experts say, is deliberately unglamorous: book through the source, not the share.
That advice applies well beyond one clinic. Across Canada, patients book flu shots, blood tests, and specialist appointments through links passed along in group chats and community pages, and most check them only when something goes wrong. The defence is not a cleverer booking platform. It is a habit of checking where the link came from before handing it personal details.
For patients, the checklist is short: book through the clinic’s own phone number or the link on its official notice, be suspicious of any booking page that asks for a health card number online, and check that a confirmation comes from the clinic’s own address. For clinics, it is equally simple: publish one official link, say clearly where it will come from, and give patients a simple way to report a copy.
The fictional centre says affected patients have been offered help rebooking for real, and the copycat page has been reported for removal.
The shots were free. The booking page charged them everything it could collect. And the difference — one link, checked before the details were entered — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.
LETHBRIDGE, Alta. — November 2, 2026 — The job looked perfect, and that was the first warning sign nobody noticed. A warehouse supervisor role, close to home, good pay, immediate start — and an application form that asked for everything. For job seekers in Lethbridge, the fictional Alberta city at the centre of the story, the posting on a copycat recruitment site felt like a lucky break. It was not hiring anyone. It was collecting them.
The site looked like a real staffing agency’s page, down to the job board layout, the company descriptions, and the application button. Applicants uploaded a résumé, then were asked to complete a “pre-employment verification” step: a photo of government ID, a home address, a date of birth, and bank details for “direct deposit setup.” The form said the information was needed before an interview could be scheduled. There was never going to be an interview.
The job had not been filled. It had never existed.
According to the fictional account, the pattern emerged only when several applicants compared notes. They had all applied for different roles — supervisor, driver, office clerk — through what looked like different employers, but the verification forms were identical, the confirmation emails came from the same misspelled domain, and none of them ever heard back. One applicant grew suspicious when the “recruiter” asked for a photo of both sides of an ID card before any phone call had taken place, and posted a warning in a local job-seekers group. Within a day, dozens of others recognised the same form.
“We were just trying to find work,” said Elena Marsh, a fictional Lethbridge job seeker who applied for the supervisor role. “You expect a job application to ask about your experience. You don’t expect it to ask for your ID and your bank account before anyone has even spoken to you. By the time I realised, I had already sent it all.”
Fake job postings are a quiet, growing target for identity theft.
Cybersecurity advisors say job scams are attractive precisely because they exploit hope and urgency. People looking for work are motivated to respond quickly, to share personal details, and to trust a professional-looking posting — especially when it promises an immediate start. An attacker needs only a copied job board, a plausible employer name, and a form that asks for one document too many.
“The application did exactly what it was designed to do. It asked, politely, for everything,” said one cybersecurity advisor familiar with recruitment fraud cases. “A real employer verifies identity late in the hiring process, after interviews, not before the first conversation. The fake posting reversed that order — and applicants, eager to move fast, followed it.”
In this fictional case, the damage was not a single dramatic breach. Applicants’ IDs, addresses, and banking details were harvested in bulk, and several people later found accounts opened or probed in their names. The harm was compounded by embarrassment: people who had been job-hunting for months were reluctant to admit they had been fooled, and some waited weeks before reporting it.
Local employment advisors say they have since changed how they warn job seekers. Listings shared through community boards now carry a short checklist: a real recruiter will not ask for government ID or bank details before an interview, a job posting should link back to a verifiable employer website and phone number, and any application that demands sensitive documents upfront should be stopped and reported. Applicants are also being urged to check the sender’s domain letter by letter — the fake site’s address differed from the real agency’s by a single swapped character.
The fix, experts say, is deliberately unglamorous: verify the employer before you verify yourself.
That advice applies well beyond one city. Across Canada, job boards and social media are filled with postings that look legitimate, and most applicants have no easy way to tell a copied listing from a real one. The defence is not a cleverer job board. It is a pause before the sensitive step.
For job seekers, the checklist is short: never send a photo of ID or bank details before an interview, confirm the employer through its official website or a listed phone number — not a number from the posting itself — and treat any “immediate start, verification first” message as a red flag. For employers and job boards, it is equally simple: publish a clear statement of what you will never ask for upfront, verify postings before they go live, and give applicants a simple way to report a suspicious listing.
Affected applicants in this fictional case are being urged to place fraud alerts on their credit files, monitor bank statements, and report the postings to the job boards that carried them.
The job looked perfect. The application asked for everything. And the difference — one verification step, demanded before any human had spoken — was all it took.
Watching the perimeter — and what slips past it.
ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.

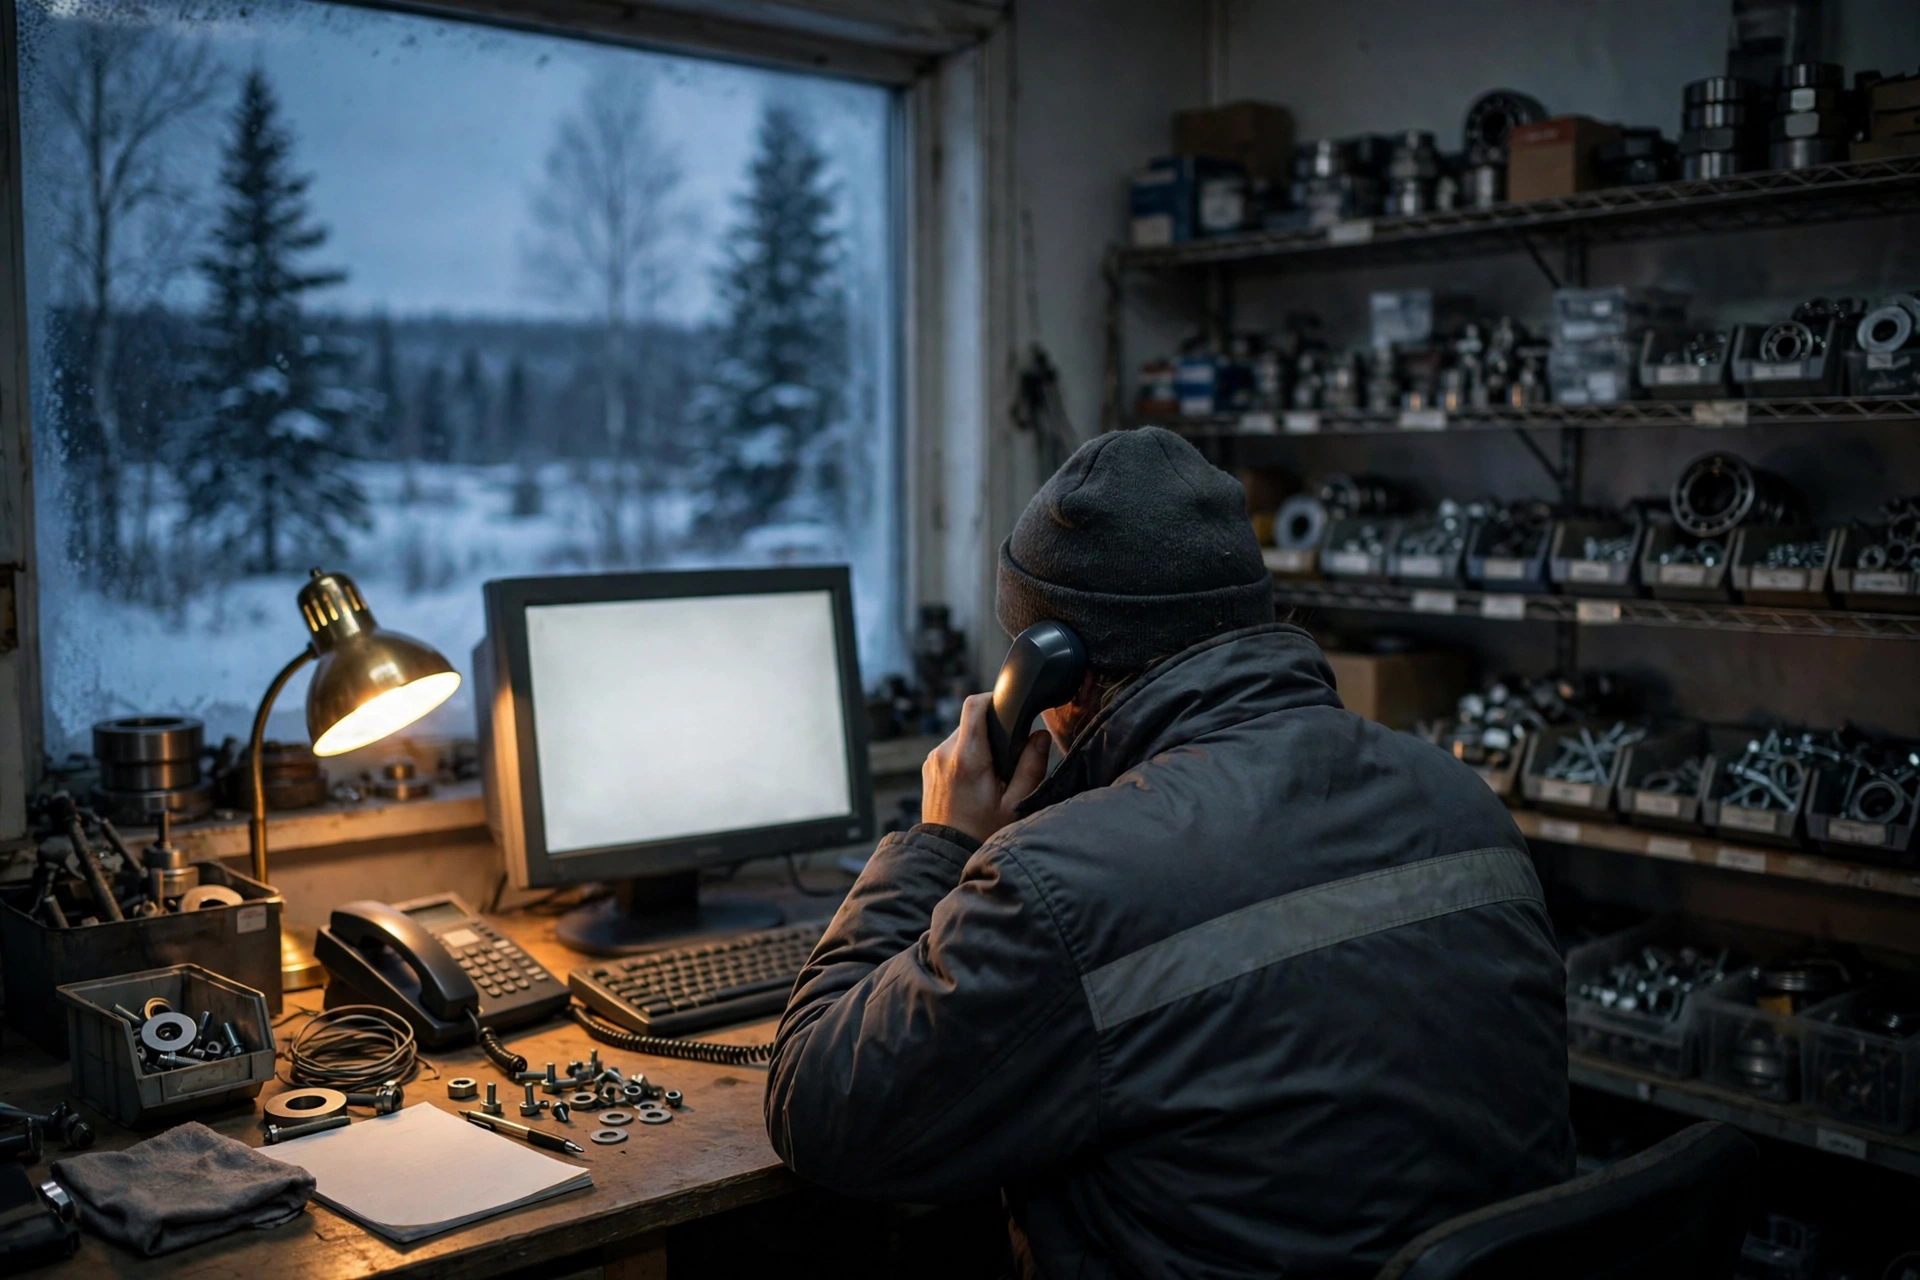
SUDBURY, Ont. — October 30, 2026 — The call sounded exactly like the boss. Same cadence, same turns of phrase, same tired joke about month-end paperwork. The accounts clerk at Northpine Industrial Supply, the fictional Sudbury supplier at the centre of the story, had no reason to doubt the voice on the line — until the request itself did not add up.
The caller, claiming to be the company’s fictional owner, asked for an urgent payment to a new supplier account, to be sent before the bank’s cut-off that afternoon. The amount was large, the account was unfamiliar, and the reason — a rush order that had supposedly changed vendors overnight — had never been mentioned in any meeting, email, or order sheet.
The voice was a clone. The boss had made no such call.
According to the fictional company’s account, the clerk paused instead of paying. She told the caller she would need to confirm the change through the company’s usual approval channel, and the line went dead. A quick check with the real owner — who was, at that moment, on a plant floor with no phone in hand — confirmed what the clerk already suspected: the call was fake.
“We train people to spot a strange email. Nobody trained us to doubt a familiar voice,” said Mara Ellison, Northpine’s fictional operations lead. “It sounded like him. It even sounded rushed in the way he sounds when he’s rushed. The only thing that saved us was that the payment itself didn’t fit the story.”
Voice cloning has turned a familiar voice into a forgery anyone can play back.
Cybersecurity advisors familiar with voice-fraud cases say the technology behind the call is no longer exotic. A short sample of a person’s voice — from a video, a voicemail greeting, a conference recording, or a social media clip — can be enough to build a convincing imitation, and the imitation can then be steered live through a phone call. The target is rarely the technology. It is the trust that a voice carries.
“The phone used to be the verification,” said one cybersecurity advisor familiar with small-business fraud cases. “If you recognized the voice, you believed the instruction. That shortcut is gone now. A voice proves nothing on its own — it is a claim, just like an email address, and it needs a second check.”
In this fictional case, the warning signs were subtle. The caller knew the owner’s name and the company’s month-end routine, but not the name of the clerk’s usual approver. The new account details arrived by a separate message, not through the company’s vendor system. And the urgency — pay before cut-off, don’t wait for paperwork — was designed to push the clerk past the pause that saved the payment.
Northpine says it has since changed its payment process. No payment instruction given by phone is acted on without a callback to a number already on file, and no vendor bank details change without a second person confirming them through a different channel. Staff have also been told to treat any urgent, out-of-process payment request — by voice, email, or message — as a stop-and-verify moment, no matter how familiar the sender sounds.
The fix, experts say, is deliberately unglamorous: never move money on a voice alone.
That advice applies well beyond Sudbury. Across Canada, small and mid-sized businesses still rely on phone approvals for payments, vendor changes, and rush orders, and a cloned voice can slip past every control that assumes the caller is who they sound like. The defence is not better ears. It is a process that does not depend on them.
For businesses, the checklist is short: agree a code word or callback rule for urgent payment requests, confirm any new bank details through a second, separate channel, and give staff explicit permission to slow down an urgent request without fear of getting in trouble for it. For anyone whose voice is public — owners, managers, spokespeople — it is worth remembering that every recording is now potential training material for an imitation.
Northpine says no money was lost. The payment was never sent, the fake account was reported, and the company is still reviewing how its owner’s voice sample may have been obtained.
The call sounded exactly like the boss. The boss had never called. And the difference — a pause, and a callback to a number already on file — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.

Spoofed Parking Portal Collected Drivers’ Fine Money

Spoofed Voter Portal Harvested Constituent Data

Smart Doorbells Streamed Porches to Strangers

Reddit Thread Over ‘Inventory Drift’ Surges as Canadians Vent Over Retail Glitches

Are Canadian Companies Learning from Global Cyber Attacks? Insider Insights into the Secret Downfall of Canadian Businesses

Canadian Airline NorthSky Faces Cyberattack, Disrupting Online Services


-
 Business4 weeks ago
siberX Shipping extends telephone service across Pacific trading hours
-
 Cybersecurity1 week ago
Tourists Scanned. Strangers Collected.
-
 Business1 week ago
Winter Cargo Vanishes on Paper Trail
-
 Cybersecurity1 week ago
Winnipeg Distributor Loses Payment to Impostor Email
-
 Cybersecurity2 weeks ago
Nova Scotia Town Goes Dark Overnight
-
 Cybersecurity1 week ago
Regina Pharmacy Shut Out of Its Own Prescriptions
-
 Business2 weeks ago
A Single Truck Left Shelves Bare
-
 Tech1 week ago
Cold Storage Warms While Dashboard Glows Green