Public
Spoofed Parking Portal Collected Drivers’ Fine Money

STONEBRIDGE, Ont. — November 7, 2026 — Eight hundred and sixty dollars in parking fines. Not one cent of it reached the town.
That is the total one fictional Stonebridge driver paid over three weeks, through a website that wore the town’s name, the town’s colours, and the town’s crest — and that the town had never built. The site, stonebridge-pay.ca, sat one hyphen away from the town’s real payments page. It accepted cards, issued receipts, and thanked drivers for paying promptly. The money went somewhere else entirely, and the real fines stayed unpaid.
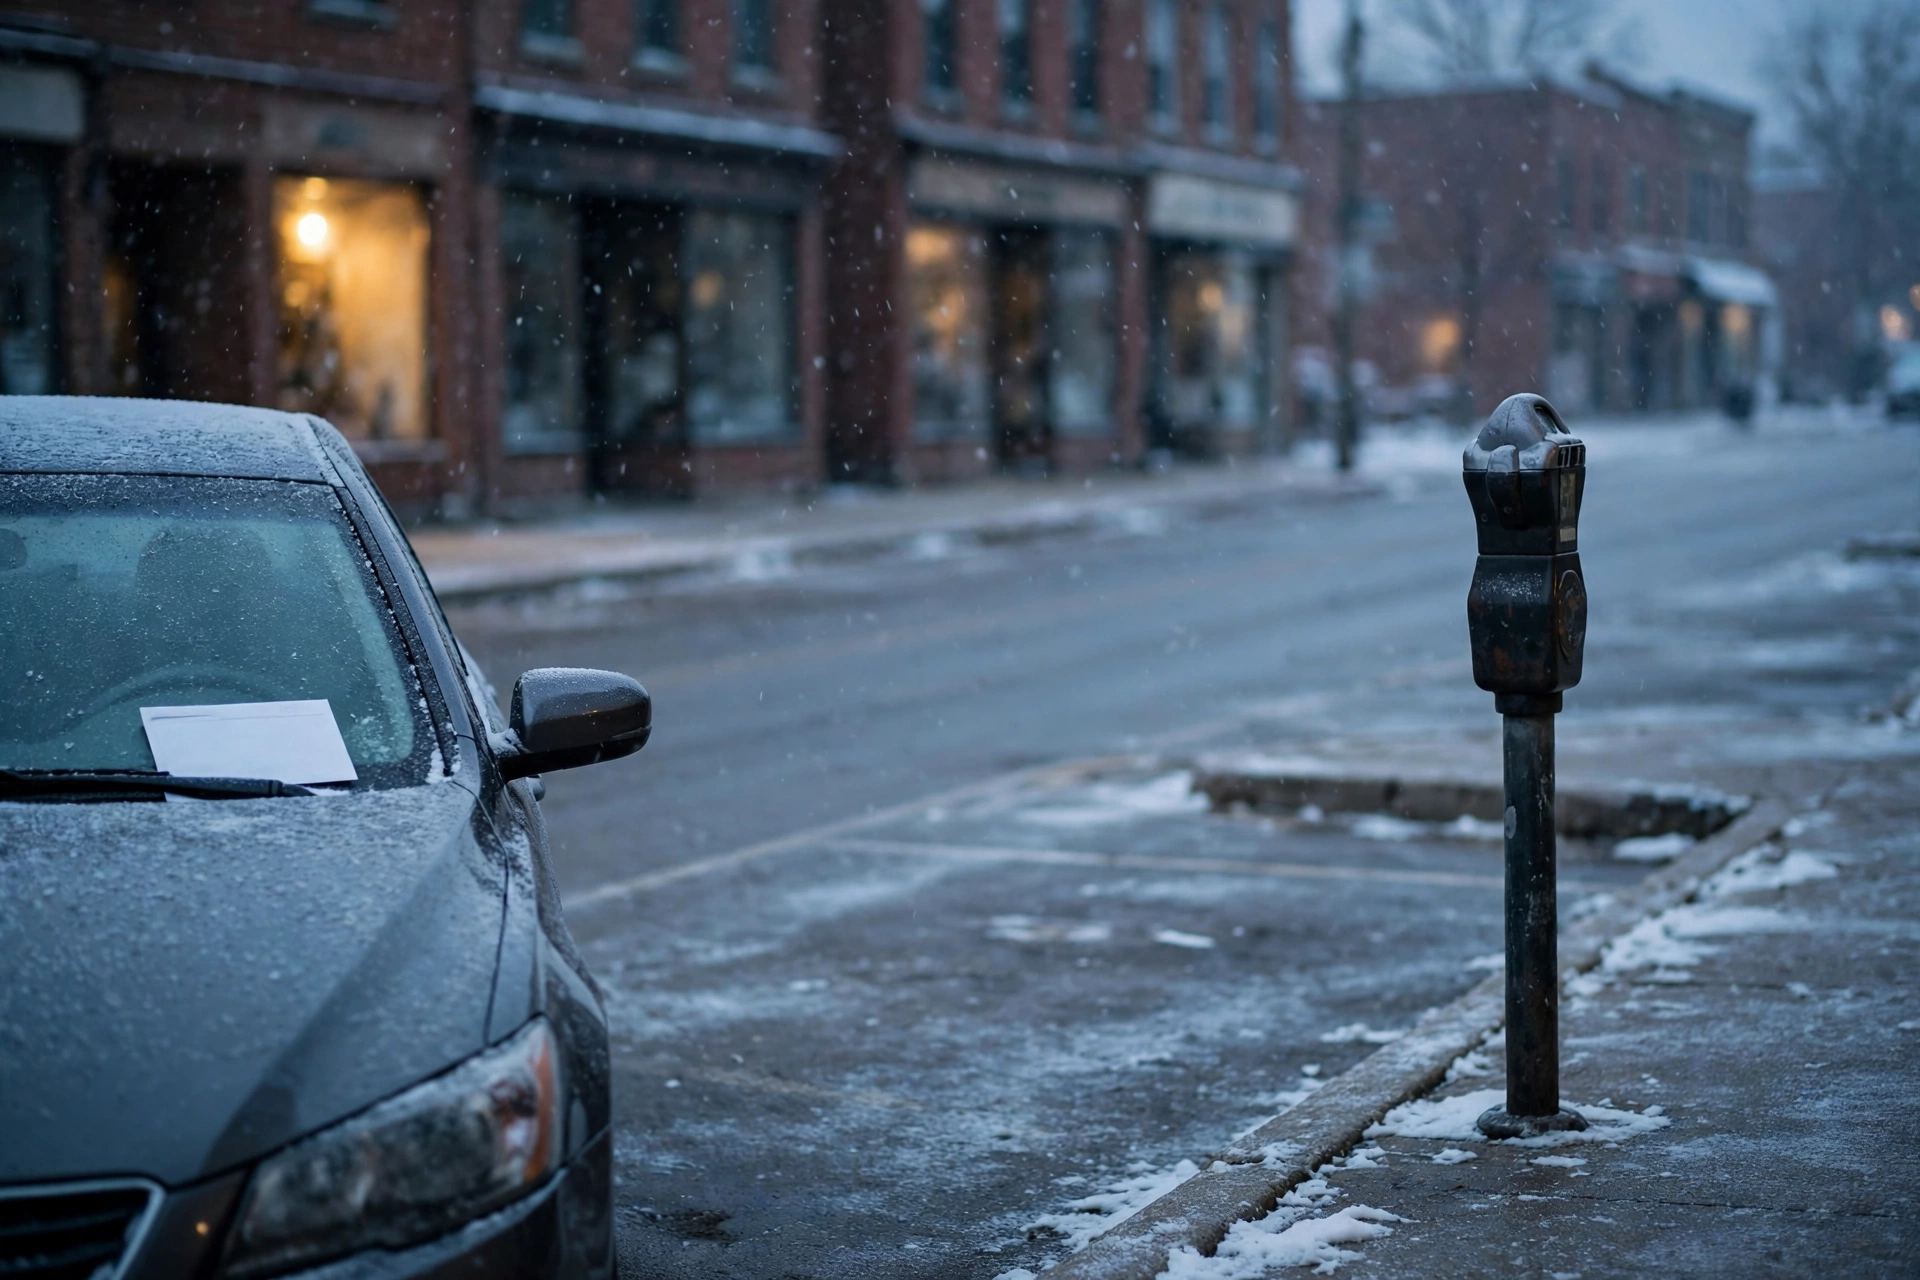
The tickets themselves were the delivery mechanism. Plain white envelopes, printed to look like the town’s parking notices, were left under windshield wipers along the main street and in the lot behind the library. Each one carried a fine amount, a plate number, and a QR code “for fast payment.” Drivers scanned the code in the moment — standing in the cold, keys in hand, keen to get the fine settled before it grew — and the code took them straight to the copycat.
Nobody hacked the town’s payment system. The town’s parking records were never touched. The copycat simply stood next to the real thing, in the same colours, and collected the fines the town was owed — while the town, unaware, kept adding late fees to accounts its own residents believed were settled.
The town never sent the tickets. The tickets came to the drivers.
According to the fictional residents who spoke to ODTN News, the first sign of trouble was a second notice. Samira Haddad, a fictional Stonebridge resident, paid two fines through the site in October and thought the matter closed — until a letter arrived saying both fines were now overdue, with late fees attached. She called the town office, receipt numbers in hand. The town had no record of either payment.
“I paid it the same day I got the ticket,” said Haddad. “The site had the town’s crest, the right colours, the right fine amounts. It gave me a receipt with a number on it. I did everything you are supposed to do when you get a ticket — pay it quickly and keep the receipt. Then the town told me I still owed the money, plus late fees, because I had paid the wrong website.”
A parking ticket is a deadline with a QR code on it — and deadlines make people scan first and check later.
Municipal-payments advisors say parking fines are attractive precisely because they come with urgency built in. A fine grows if it is not paid, so drivers act fast, on the street, from a phone, without the pause they would take over a larger bill at home. A ticket also asks for exactly the information a thief wants: a plate number, a name, and a card. And a windshield is a trusted place — a ticket left on a car feels official in a way an email never does.
“A tax bill arrives in the mail and you read it at the kitchen table,” said Irene Kwan, a fictional municipal-payments advisor who works with small towns on their payment systems. “A parking ticket arrives on your windshield and you deal with it where you stand. That is the whole trick. The site did not need to break into anything. It just needed to be the first place a driver in a hurry landed — and to look enough like the town that nobody stopped to ask whose site it was.”
In this fictional case, the copycat stayed live for nineteen days before the town had the domain taken down. The town clerk, Martin Doyle, told residents the town never places QR codes on parking tickets, that fines are paid only through the town’s own website or in person at town hall, and that anyone who paid through the copycat should contact their bank and the town office. The town has not said how many drivers paid through the site, or how much money was collected.
The fictional residents say they have since changed how they handle tickets. Fines are now paid by typing the town’s address into a browser by hand, or in person at town hall — never through a code printed on the ticket itself. Several households have asked their banks to reverse the charges, and the town office has taken to answering the same question dozens of times a day: no, the ticket on your windshield is not necessarily from the town.
The defence is not a cleverer ticket. It is a habit of never paying a fine from a code on a windshield.
That advice applies well beyond one town’s parking fines. Across Canada, towns and cities send residents bills, tickets, and notices that all carry a link or a code and a deadline — and a copycat needs only one hyphen, or one sticker on a windshield, to stand beside the real thing. The defence is not a better website. It is a habit of reaching the payment page yourself, and of treating any code on a piece of paper left on your car as untrusted until the town confirms it.
For drivers, the checklist is short: never pay a fine by scanning a code on the ticket — type the town’s address yourself or pay in person; check that the site address matches the one on the town’s own letters, not the one on the ticket; and if you paid through a site you now doubt, call your bank and the town office the same day. For towns, it is equally simple: never put a QR code on a parking ticket, publish the real payment address everywhere, and take copycat domains down the same day they appear.
The fictional residents say the copycat site has been taken down, and the town’s real payment page is unchanged.
The fines were never paid. The money was never the town’s. And the difference — one address, typed by hand instead of scanned from a windshield — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.




GUELPH, Ont. — November 4, 2026 — The ice was booked, the kids were ready, and the confirmation email looked exactly right. When families in a fictional Guelph neighbourhood arrived for their weekend rink time, their names were not on the list at all. The booking had not been lost. The page they had booked through was never the city’s page.
The problem was not in the city’s own recreation system. It was in the link most families found first: a post shared in parents’ groups and forwarded by email, promising a simple way to reserve public skate and shinny slots. The page it led to carried the rink’s name, its schedule, and a familiar-looking booking calendar. It asked for a name, a phone number, an email address, and a payment card to hold the ice time. None of that information ever reached the city.
The ice time had not been double-booked. It had never been booked through the real system at all.
According to the fictional community association at the centre of the story, the pattern emerged only when several families compared notes at the rink door. They had all booked through the same forwarded link, but none of them appeared on the real reservation list, and none of them had received a confirmation from the city’s own address. One parent had even called the number on the fake page to ask about skate rentals, and been reassured by a polite voice that her slot was confirmed.
“We tell families to book early and show up ready to skate, and that is exactly what they did,” said Priya Sandhu, the fictional association’s recreation coordinator. “Nobody expects to have to inspect a booking page the way you would inspect a front door. But someone built a copy of our rink booking, put it where parents share links, and collected their details as they walked in.”
Copycat booking pages are a quiet, growing target for payment fraud.
Public-service and cybersecurity advisors say community bookings are attractive precisely because they are seasonal, trusted, and shared in a hurry. A rink slot does not need to be breached in the dramatic sense — an attacker only needs to copy its name and schedule onto a convincing page, and wait for a forwarded link to do the rest. Parents, meanwhile, trust a link shared by another parent far more readily than one from a stranger, especially when the page looks official and the ice time is limited.
“The page did exactly what it was designed to do. It took a booking,” said one payments-fraud advisor familiar with copycat booking cases. “The attacker did not need to break into the city’s systems. They only needed to stand between families and the real booking page, and let honest planning do the rest.”
In this fictional case, the damage was not a single dramatic theft. Individual families handed over names, phone numbers, email addresses, and, in some cases, payment-card details entered to hold a slot. The association estimates dozens of families booked through the fake page before it was reported, and several later received suspicious calls and messages using details only the fake form had collected. For the families, the loss was compounded by the moment of discovery — arriving at the rink, skates in hand, to find they had never been booked at all.
The fictional association says it has since changed how it shares booking links. Real rink links now come only from the city’s own website and the association’s own mailing list, never from a forwarded social post alone, and the association checks shared links weekly, the way it checks its rink schedule. Families who used the fake page are being asked to change any password they reused, watch for calls that quote their phone number, and check statements for small charges in the days after booking.
The fix, experts say, is deliberately unglamorous: get the link from the source, not the share.
That advice applies well beyond one rink. Across Canada, families book pools, arenas, classes, and camps through links passed along in group chats and parents’ pages, and most check them only when something goes wrong. The defence is not a cleverer booking platform. It is a habit of checking where the link came from before handing it personal details.
For families, the checklist is short: book through the city’s own website or the number printed on its official notice, be suspicious of any booking page that asks for a full payment card to hold a free or low-cost public slot, and check that a confirmation comes from the city’s own domain. For community groups, it is equally simple: publish one official link, say clearly where it will come from, and give families a simple way to report a copy.
The fictional association says affected families have been offered help rebooking for real rink time, and the copycat page has been reported for removal.
The families showed up ready to skate. The ice time they booked was never the city’s. And the difference — one link, checked before the details were entered — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.
PRINCE GEORGE, B.C. — November 1, 2026 — The Wi-Fi login page looked exactly right. It carried the library’s colours, it asked for a library card number and PIN, and it connected visitors to the internet in seconds. For regulars at Sprucewood Public Library, the fictional Prince George library at the centre of the story, there was no reason to doubt it — until staff realised the page was not theirs at all.
The network had appeared beside the library’s real Wi-Fi, with a name only one word different. Patrons who joined it were taken to a copy of the library’s sign-in screen, typed in their credentials, and were passed through to the internet as normal. Nothing failed. Nothing looked broken. The theft happened in the moment that looked most ordinary.
The login page had not been hacked. It had been imitated.
According to the fictional library’s account, the fake network was discovered only when a staff member noticed two nearly identical network names on her own phone and asked a colleague which one was real. By then, the library estimates, dozens of patrons had signed in through the copy over several days. Some had also reused the same PIN elsewhere, which is where a library login stopped being a library problem.
“We offer free Wi-Fi because people need it — for job applications, for homework, for staying in touch,” said Clara Beaumont, Sprucewood’s fictional library director. “Nobody should have to be a security expert to sit down with a laptop in a public library. But someone set a trap in the one place people expect to be safe, and it looked exactly like us.”
Public Wi-Fi is a quiet, growing target for credential theft.
Cybersecurity advisors say fake hotspots — sometimes called evil twins — are attractive precisely because they require no break-in. An attacker only needs a small device, a network name close enough to the real one, and a login page copied from the genuine sign-in screen. Visitors do the rest themselves, willingly handing over credentials to a page they believe they have used before.
“The page did exactly what it was designed to do. It asked, politely, for a login,” said one cybersecurity advisor familiar with public Wi-Fi cases. “People are trained to sign in to Wi-Fi. The attacker did not need to defeat any security — they only needed to be the first network a phone offered, with a name that looked familiar enough not to question.”
In this fictional case, the damage was not a single dramatic breach. Patrons’ library accounts were accessed, holds were changed, and a handful of people who reused their library PIN as a password elsewhere found other accounts probed as well. The library says no financial information was stored in its system, but the incident still forced it to reset credentials, warn patrons, and explain to regulars why a page they trusted had not been its own.
Sprucewood says it has since changed how its Wi-Fi works. The real network name is now posted at every entrance and on every table, staff can confirm it on request, and the sign-in page no longer asks for a full library card number and PIN on public Wi-Fi — a simpler guest pass is issued at the desk instead. The library has also added a warning to its login screen: if a sign-in page appears before you have chosen the network name posted in the building, stop and ask staff.
The fix, experts say, is deliberately unglamorous: check the network name before you check the login box.
That advice applies well beyond one library. Across Canada, libraries, community centres, cafés, and transit hubs offer free Wi-Fi that visitors join without a second thought, and most of those networks are easy to imitate with a similar name. The defence is not better Wi-Fi. It is proof of which network is real.
For public spaces, the checklist is short: post the exact network name where people can see it, never ask for sensitive credentials on a public Wi-Fi login, and give staff a simple script for the question “is this your Wi-Fi?” For visitors, it is equally simple: join only the network name posted in the building, never reuse a PIN or password from another account on a Wi-Fi login, and if a login page appears unprompted, close it and ask staff before typing anything.
Sprucewood says patron credentials caught in the fake sign-in have been reset, and the library is working with its internet provider to monitor for lookalike networks near the building.
The page looked like the library’s. The network name almost was. And the difference — one word, checked against a sign on the wall — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.

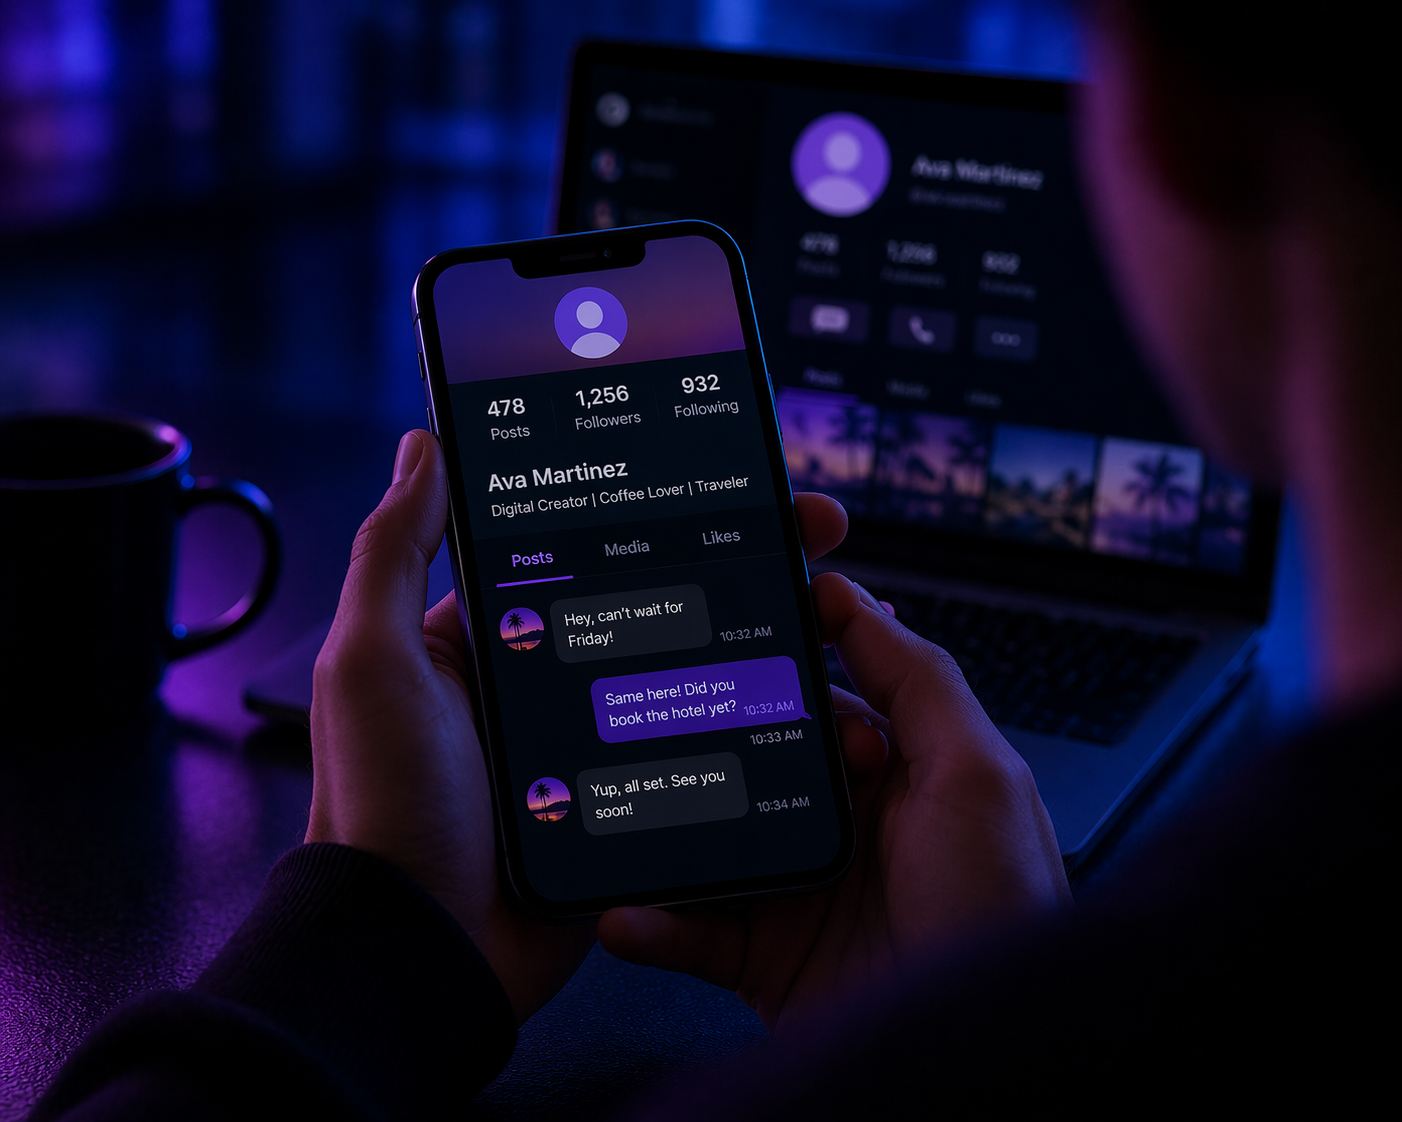
April 16, 2026 — A technical malfunction on the social platform Veya briefly exposed user accounts earlier today, with some individuals reporting that they were able to view messages and profile information that did not belong to them. The issue occurred during what the company described as a routine system update and appears to have affected a portion of active users before being quickly identified and contained.
In a statement issued shortly after the incident, Veya confirmed that the problem has now been resolved and emphasized that there is no evidence of a cyberattack or unauthorized external access. Instead, the company attributed the exposure to an internal system error, though it has not disclosed how many users were impacted or the full extent of the data that may have been visible.
Despite the short duration of the incident, the nature of the exposure has raised concern among cybersecurity and privacy experts. Users reported seeing fragments of private conversations and profile details associated with other accounts, pointing to a temporary breakdown in the platform’s ability to properly isolate user data — a core function of any multi-user system.
While Veya has not released detailed technical findings, early indications suggest the issue may have stemmed from how user sessions were handled during the update process. Platforms like Veya rely on session tokens to verify identity and ensure that users only access their own data. If those tokens are mismanaged — whether through improper reassignment, delayed refresh cycles, or synchronization issues during deployment — users can momentarily be granted access to information tied to another account. In parallel, caching mechanisms designed to improve performance can also introduce risk if stored data is incorrectly served to the wrong user during periods of system change.
Incidents of this nature, while not malicious, underscore the complexity of maintaining strict data boundaries at scale, particularly during live updates where systems are actively being modified. Even brief lapses can result in unintended exposure, and experts note that the impact of such events is not necessarily limited by their duration. Information that is visible, even for seconds, can be captured, recorded, or retained.
Veya is advising users to review their recent account activity and take standard security precautions, including logging out of active sessions and updating passwords. While there is no indication of ongoing risk, the incident highlights the importance of vigilance at both the user and platform level.
As platforms continue to evolve and deploy updates at increasing speed, events like this serve as a reminder that not all data exposures stem from external threats. In some cases, the risk lies within the systems themselves — in how they manage identity, access, and the invisible boundaries that keep user data separate.
For users, the expectation remains unchanged: that their information is secure and accessible only to them. For platforms, maintaining that expectation is becoming an increasingly complex challenge.
Reporting where the public speaks loudest — online and unfiltered. — Jamie Mora

Spoofed Parking Portal Collected Drivers’ Fine Money

Spoofed Voter Portal Harvested Constituent Data

Smart Doorbells Streamed Porches to Strangers

Reddit Thread Over ‘Inventory Drift’ Surges as Canadians Vent Over Retail Glitches

Are Canadian Companies Learning from Global Cyber Attacks? Insider Insights into the Secret Downfall of Canadian Businesses

Canadian Airline NorthSky Faces Cyberattack, Disrupting Online Services


-
 Business4 weeks ago
siberX Shipping extends telephone service across Pacific trading hours
-
 Cybersecurity1 week ago
Tourists Scanned. Strangers Collected.
-
 Business1 week ago
Winter Cargo Vanishes on Paper Trail
-
 Cybersecurity1 week ago
Regina Pharmacy Shut Out of Its Own Prescriptions
-
 Cybersecurity2 weeks ago
Nova Scotia Town Goes Dark Overnight
-
 Cybersecurity1 week ago
Winnipeg Distributor Loses Payment to Impostor Email
-
 Business2 weeks ago
A Single Truck Left Shelves Bare
-
 Tech1 week ago
Cold Storage Warms While Dashboard Glows Green