Cybersecurity
Colonial Pipeline Wasn’t Just a Ransomware Story. It Was a Warning for Every Pipeline Operator.

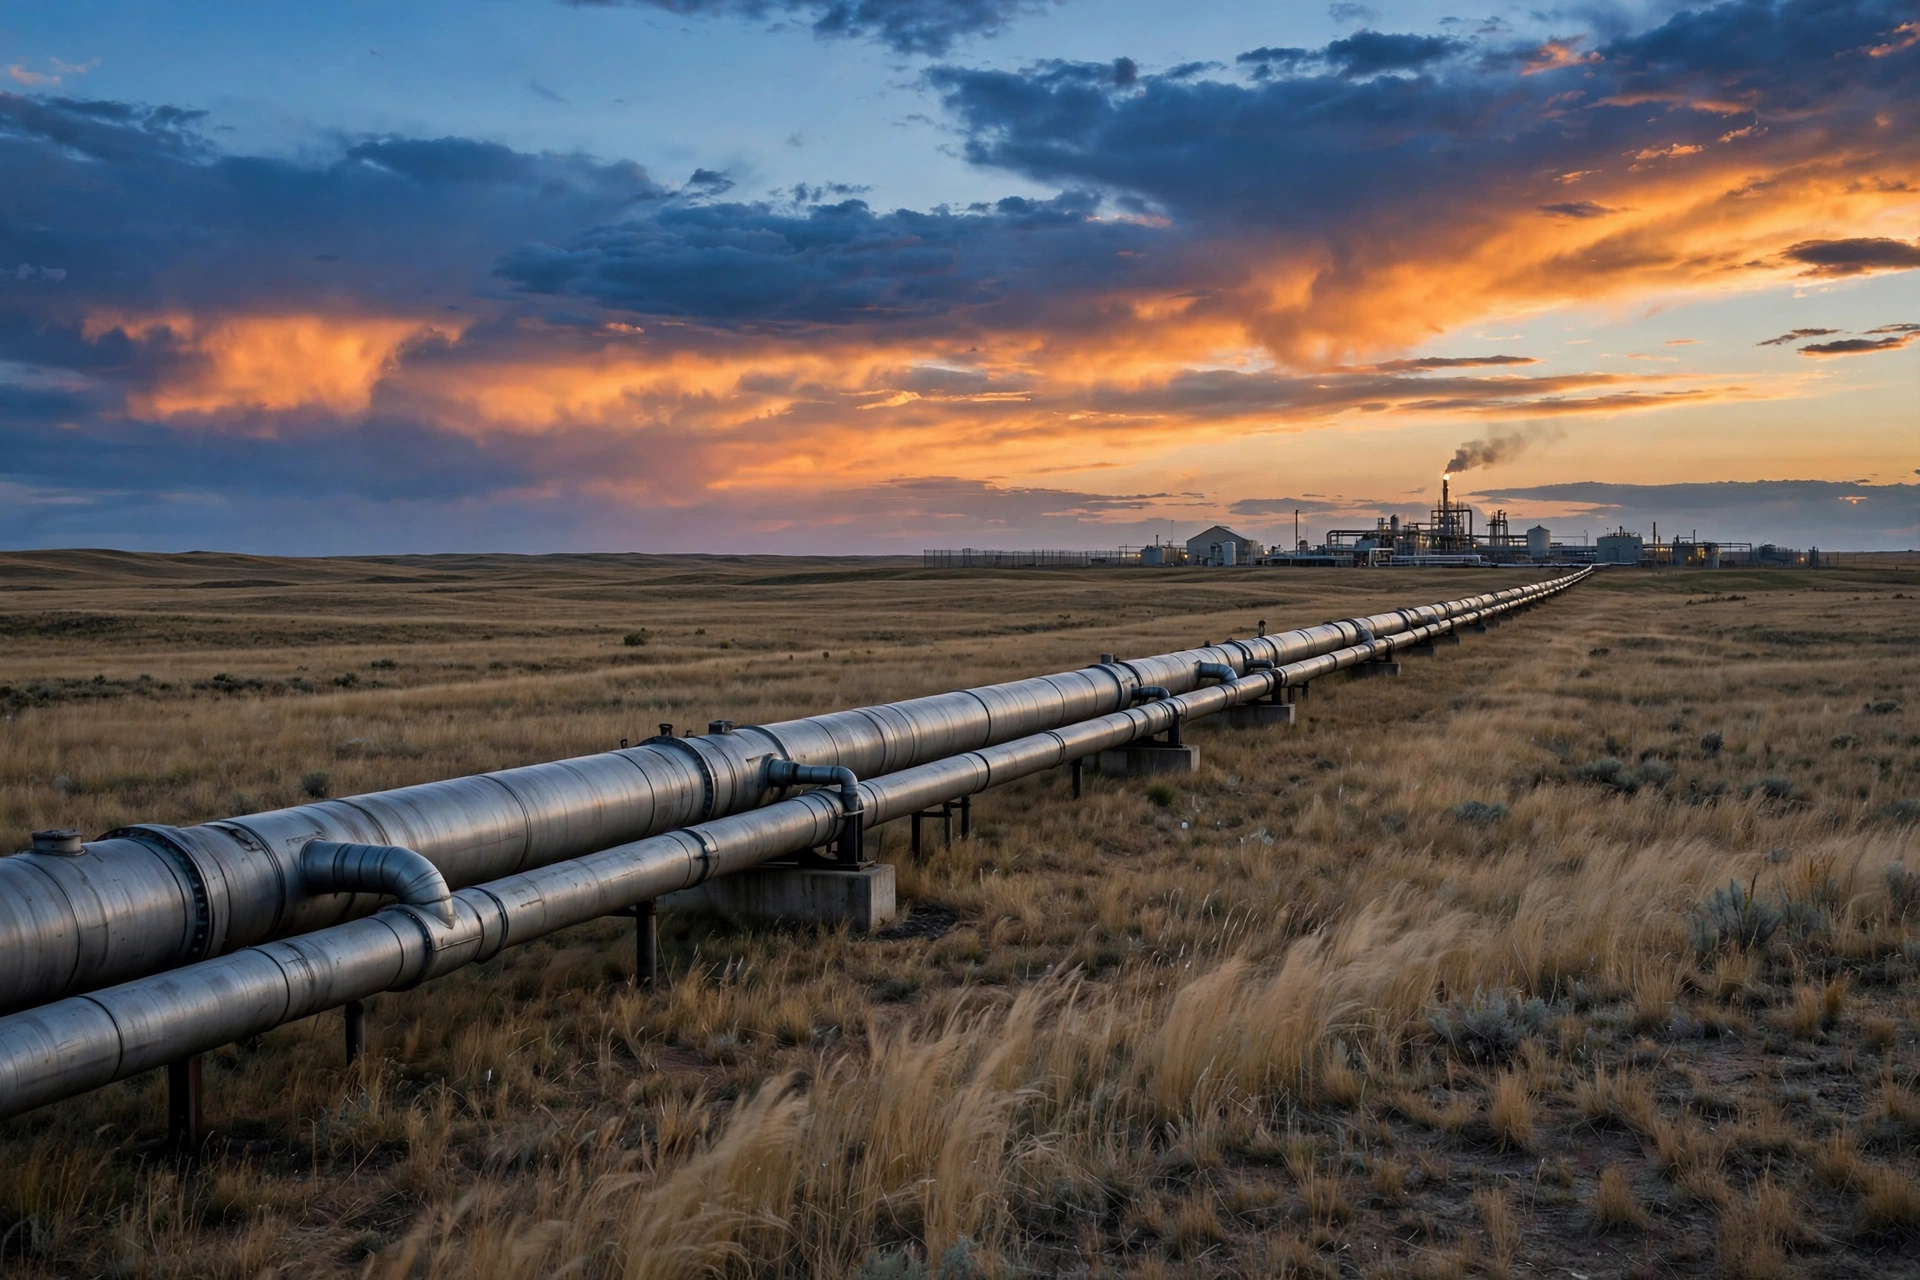
In May 2021, a single compromised password shut down the largest fuel pipeline in the United States.
Colonial Pipeline carries refined fuel across 5,500 miles from Texas to New York, supplying roughly 45 percent of the fuel consumed on the U.S. East Coast. On May 7, 2021, the company discovered it had been hit by ransomware from the DarkSide group. Within hours, Colonial took its pipeline offline — not because the attackers had reached the pipeline’s operational controls, but because the company could no longer trust the systems that billed for, scheduled, and managed the fuel moving through it.
The pipeline stayed down for six days. Gas stations ran dry. Airlines rerouted. Panic buying spread across the Southeast. The U.S. government declared a regional emergency. Colonial paid a $4.4 million ransom in Bitcoin — part of which the FBI later recovered — and spent weeks rebuilding systems and restoring confidence.
The attackers never needed to touch a valve, a pump, or a pressure sensor. They only needed to hit the business systems around them, and the pipeline stopped anyway.
That is the lesson that matters most for Canada, and for Alberta in particular.
Threat actors are looking at critical infrastructure — and pipelines are the leverage
Pipelines, power grids, water systems, and oil sands operations are not targeted because they are easy. They are targeted because they are essential. A shutdown does not need to cause physical damage to cause national disruption. It only needs to stop the flow — of fuel, of power, of water — for long enough that the public, the markets, and governments feel it.
That leverage is exactly what ransomware groups and state-linked actors are looking for. In recent years, security researchers and government agencies have warned repeatedly that operational technology (OT) — the systems that run physical processes — is now firmly in scope for attackers who once focused only on IT networks. The boundary between IT and OT, long treated as a wall, has become a bridge: remote monitoring, cloud dashboards, vendor access, and connected sensors have all made operations more efficient, and more exposed.
Colonial is the case study because it proved the point without a single OT breach. The next attack may not be so restrained.
What Colonial actually got wrong
The Colonial attack did not start with a sophisticated exploit. Investigators later found the entry point was a legacy virtual private network (VPN) account whose password had leaked, with no multi-factor authentication in place. One credential, one missing control, and the attackers were inside the network.
From there, the lessons are familiar — which is precisely why they are worth repeating:
1. A single credential should never be enough. Multi-factor authentication on every remote access point, especially VPNs and vendor accounts, is not a best practice anymore. It is the baseline. Colonial’s missing MFA turned a leaked password into a company-wide crisis.
2. IT and OT must be segmented — and that segmentation must be tested. Colonial shut its OT systems down as a precaution because it could not be certain the infection had not spread. Operators who cannot prove their OT environment is isolated from their IT environment will face the same choice: shut down, or gamble.
3. Manual operations are a capability, not a fallback. When digital systems go down, can a pipeline still run safely by hand? Can staff operate valves, monitor pressure, and track product without the software they rely on every day? If that has never been practiced, the answer is no — and the shutdown lasts longer.
4. The decision to shut down is the hardest decision, and it must be made in advance. Colonial’s leadership had hours to decide whether to halt a pipeline that supplied millions of people. That decision should not be improvised in a crisis. It should be rehearsed, with clear authority, clear triggers, and a clear understanding of what “safe shutdown” actually means.
5. Paying the ransom does not solve the problem. Colonial paid, and still spent weeks recovering. Ransomware payment is a business decision with legal, ethical, and operational consequences — and it guarantees nothing about decryption, data deletion, or whether the same group will return.
The warning for Canadian operators
Canada’s energy infrastructure faces the same pressures: aging OT systems, connected operations, third-party vendors with remote access, and a workforce stretched between keeping systems running and keeping them secure.
The warning is not that a Colonial-style attack will happen here tomorrow. It is that the conditions that made Colonial possible — a leaked credential, a flat network, an untested shutdown plan — exist in operations across the country right now.
Threat actors do not need to understand pipeline engineering to shut a pipeline down. They need to understand where the business systems end and the operational systems begin — and where the two are still connected.
What to do before the next one
For pipeline operators, utilities, and the teams that defend them, the work is unglamorous and urgent:
- Enforce multi-factor authentication on every remote and vendor account, with no legacy exceptions.
- Map and segment IT from OT, and prove the segmentation works — don’t assume it.
- Practice manual operations and safe shutdowns, so a digital outage does not become a physical crisis.
- Rehearse the shutdown decision in a tabletop exercise, with the people who would actually have to make it in the room.
- Treat third-party and vendor access as a front door, with monitoring, time limits, and revocation plans.
None of this is new. All of it is still unfinished in too many operations.
Why this matters now
That is the scenario at the heart of Operation: Defend the North in Calgary on Friday, November 13, 2026, at Bow Valley College — a hands-on War Room Simulation where leaders face a crisis in real time and have to make the decisions Colonial’s leaders faced, under pressure, with incomplete information.
The point of the exercise is not to relive 2021. It is to make sure the next time a pipeline operator in Canada faces that choice, the decision has already been made, the manual procedures have already been practiced, and the shutdown — if it has to happen — is controlled, safe, and short.
Colonial Pipeline was a warning. Five years on, the question is not whether threat actors are still looking at critical infrastructure. They are. The question is whether operators have learned the lessons fast enough.
Operation: Defend the North 2026 — Calgary, Friday, November 13, 2026, 9:00 AM–5:00 PM, Bow Valley College, 345 6 Ave SE, Calgary. https://siberx.org/event/operation-defend-the-north-2026-calgary/




CEDAR HOLLOW, Ont. — November 10, 2026 — The text arrived at 11:47 p.m., twelve hours before Maya Chen’s first final exam. It said her exam room had changed, and gave her a link to confirm the new one. Chen, a first-year student at Cedar Hollow University, tapped it, typed in her student login, and went to sleep. By morning, her password no longer worked — and neither did the logins of more than two hundred of her classmates.
The link did not lead to the university’s exam portal. It led to a copy, built to look like the real one down to the crest, the colours, and the “confirm your exam schedule” button. Students who signed in handed over their usernames and passwords. Within hours, the attackers had used those logins to change the passwords, locking the real owners out of their exam schedules, course pages, and student email — days before final exams begin.
More than two hundred students lost access to their exams in a single night — and none of them had clicked anything unusual.
The messages arrived as texts and emails, timed for the night before exam week, when students were already anxious and checking their phones late. Each one warned of a changed exam room or a schedule update, and each one linked to the copycat portal. The university says its real exam portal never sends schedule changes by text, and never asks students to log in from a link in a message. But at midnight before finals, few students stopped to check.
“I did what the message told me to do, because it told me to do it the way the university always does,” Chen said. “It had the exam schedule, it had my course code, it even had my professor’s name. I thought I was being responsible. Then I woke up locked out of everything.”
Cedar Hollow University says it has reset the affected accounts, restored access to exam schedules, and confirmed that no exam has been missed. But the university’s IT director, Priya Sandhu, said the lockout was the point — not a side effect. “The attackers didn’t want the passwords for their own sake,” Sandhu said. “They wanted the accounts. A student account opens the exam portal, the email, the library, the financial aid page. Lock the student out, and you hold everything they need for exam week.”
A student login is a master key — and this one opened every door the university has.
Student accounts are a soft target precisely because they unlock so much with a single sign-in. One username and password reaches the exam schedule, the grades, the email, and in many cases the financial aid and fee records. Students reuse those passwords elsewhere, share them with study groups, and rarely turn on multi-factor authentication. And during exam week, a message about a changed exam room arrives at the exact moment a student is least likely to question it.
“Attackers don’t need a sophisticated hack when the calendar does the work for them,” said Daniel Okafor, a fictional cybersecurity advisor who works with colleges on account security. “Exam week is the one week of the year when every student is expecting an urgent message from their university, and every one of them is too tired to check the sender. The portal didn’t have to be perfect. It only had to arrive at midnight.”
In this fictional case, the copycat portal stayed live for nine days before it was taken down. The university says it has since forced a password reset for all students, turned on multi-factor authentication for exam portal access, and is warning students to reach the portal only by typing the address themselves — never from a link in a text or an email. It has not said how many accounts were harvested in total, or whether any student’s financial information was reached.
The fictional students say they have since changed how they treat their university logins. Passwords are unique to the university account. Multi-factor authentication is on. And no exam message is ever trusted from a link — the schedule is checked by opening the portal directly, the same way every time.
The defence is not a sharper eye for fake portals. It is never logging in from a link at all.
That advice applies well beyond one campus. Across Canada, colleges and universities all run portals that hold a student’s exams, grades, email, and aid behind a single login — and a copycat needs only a well-timed message to stand beside the real thing. The defence is not a cleverer warning email. It is a habit of typing the address yourself, and of treating any login link in a message as untrusted until the university confirms it.
For students, the checklist is short: never log in from a link in a text or email, even one that looks like it came from your school; give your student account its own password and turn on multi-factor authentication; and if a message says your exam changed, check the portal by opening it yourself. For universities, it is equally simple: never send login links by text, publish the real portal address everywhere, and take copycat portals down the same day they appear.
The fictional students say the copycat portal has been taken down, and the real Cedar Hollow University exam portal is unchanged.
The passwords were never the students’. The accounts were never the attackers’. And the difference — one login, typed in directly instead of tapped from a message — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.
BARRIE, Ont. — November 5, 2026 — By the time the real clinic opened its doors on Monday morning, 214 people had already booked their flu shots — through a website the clinic had never built. The appointments were confirmed, the reminders were sent, and the patients were told to bring their health cards. The clinic itself had no record of any of them.
The booking page had not broken into anything. It had simply arrived first. A copy of a fictional Barrie community health centre’s flu-shot clinic, complete with the centre’s name, its hours, and a reassuring note that appointments were filling fast, it asked each visitor for a name, a date of birth, a phone number, an email address — and a health card number, supposedly to confirm eligibility. The centre never asks for a health card number online.
The clinic had not been hacked. Its appointment book had been replaced.
According to the fictional health centre at the centre of the story, the pattern surfaced only when patients began arriving with confirmation emails the centre had never sent. The messages came from an address close to the centre’s own, and the page they linked to carried the centre’s colours and its flu-season poster. Patients who called the number on the fake page were told their appointment was confirmed and to arrive ten minutes early. None of them appeared on the centre’s real schedule.
“We run a free clinic. Nobody pays, and nobody books with a health card number,” said Elena Marsh, the fictional centre’s operations coordinator. “But the page looked like ours, it used our name, and it reached people through the same parent groups and seniors’ chats where we share our real notices. People did exactly what we ask them to do — they booked early. They just booked with the wrong page.”
A health card number, paired with a name and a date of birth, is a key to identity theft.
Health-privacy and cybersecurity advisors say booking portals are attractive precisely because they are routine, trusted, and time-sensitive. A flu clinic does not need to be breached in the dramatic sense — an attacker only needs to copy a trusted local service onto a convincing page, and wait for a forwarded link to do the rest. Patients, meanwhile, trust a booking link shared by a neighbour or a community group far more readily than one from a stranger, especially when the appointment is free and the slots are supposedly limited.
“The page did exactly what it was designed to do. It collected the details that open doors,” said one health-privacy advisor familiar with copycat booking cases. “A health card number on its own is one thing. A health card number with a name, a date of birth, a phone number, and an email address is a full identity kit — enough to impersonate a patient, open accounts, and answer security questions.”
In this fictional case, the damage was not a single dramatic theft. More than two hundred people handed over health card numbers and dates of birth before the page was reported, and several later received suspicious calls quoting details only the fake booking form had collected. For the patients, the loss was compounded by the moment of discovery — arriving for a shot that was never booked, and learning that the details they had given away could not be taken back.
The fictional centre says it has since changed how it takes bookings. Flu-shot appointments now come only through the centre’s own phone line and the link printed on its notice board, never through a forwarded message alone, and staff check shared links the way they check their appointment list. Patients who used the fake page are being asked to watch for calls that quote their health card number, to report any unexpected mail or account activity, and to contact the centre directly if anyone claims to be following up on their booking.
The fix, experts say, is deliberately unglamorous: book through the source, not the share.
That advice applies well beyond one clinic. Across Canada, patients book flu shots, blood tests, and specialist appointments through links passed along in group chats and community pages, and most check them only when something goes wrong. The defence is not a cleverer booking platform. It is a habit of checking where the link came from before handing it personal details.
For patients, the checklist is short: book through the clinic’s own phone number or the link on its official notice, be suspicious of any booking page that asks for a health card number online, and check that a confirmation comes from the clinic’s own address. For clinics, it is equally simple: publish one official link, say clearly where it will come from, and give patients a simple way to report a copy.
The fictional centre says affected patients have been offered help rebooking for real, and the copycat page has been reported for removal.
The shots were free. The booking page charged them everything it could collect. And the difference — one link, checked before the details were entered — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.
LETHBRIDGE, Alta. — November 2, 2026 — The job looked perfect, and that was the first warning sign nobody noticed. A warehouse supervisor role, close to home, good pay, immediate start — and an application form that asked for everything. For job seekers in Lethbridge, the fictional Alberta city at the centre of the story, the posting on a copycat recruitment site felt like a lucky break. It was not hiring anyone. It was collecting them.
The site looked like a real staffing agency’s page, down to the job board layout, the company descriptions, and the application button. Applicants uploaded a résumé, then were asked to complete a “pre-employment verification” step: a photo of government ID, a home address, a date of birth, and bank details for “direct deposit setup.” The form said the information was needed before an interview could be scheduled. There was never going to be an interview.
The job had not been filled. It had never existed.
According to the fictional account, the pattern emerged only when several applicants compared notes. They had all applied for different roles — supervisor, driver, office clerk — through what looked like different employers, but the verification forms were identical, the confirmation emails came from the same misspelled domain, and none of them ever heard back. One applicant grew suspicious when the “recruiter” asked for a photo of both sides of an ID card before any phone call had taken place, and posted a warning in a local job-seekers group. Within a day, dozens of others recognised the same form.
“We were just trying to find work,” said Elena Marsh, a fictional Lethbridge job seeker who applied for the supervisor role. “You expect a job application to ask about your experience. You don’t expect it to ask for your ID and your bank account before anyone has even spoken to you. By the time I realised, I had already sent it all.”
Fake job postings are a quiet, growing target for identity theft.
Cybersecurity advisors say job scams are attractive precisely because they exploit hope and urgency. People looking for work are motivated to respond quickly, to share personal details, and to trust a professional-looking posting — especially when it promises an immediate start. An attacker needs only a copied job board, a plausible employer name, and a form that asks for one document too many.
“The application did exactly what it was designed to do. It asked, politely, for everything,” said one cybersecurity advisor familiar with recruitment fraud cases. “A real employer verifies identity late in the hiring process, after interviews, not before the first conversation. The fake posting reversed that order — and applicants, eager to move fast, followed it.”
In this fictional case, the damage was not a single dramatic breach. Applicants’ IDs, addresses, and banking details were harvested in bulk, and several people later found accounts opened or probed in their names. The harm was compounded by embarrassment: people who had been job-hunting for months were reluctant to admit they had been fooled, and some waited weeks before reporting it.
Local employment advisors say they have since changed how they warn job seekers. Listings shared through community boards now carry a short checklist: a real recruiter will not ask for government ID or bank details before an interview, a job posting should link back to a verifiable employer website and phone number, and any application that demands sensitive documents upfront should be stopped and reported. Applicants are also being urged to check the sender’s domain letter by letter — the fake site’s address differed from the real agency’s by a single swapped character.
The fix, experts say, is deliberately unglamorous: verify the employer before you verify yourself.
That advice applies well beyond one city. Across Canada, job boards and social media are filled with postings that look legitimate, and most applicants have no easy way to tell a copied listing from a real one. The defence is not a cleverer job board. It is a pause before the sensitive step.
For job seekers, the checklist is short: never send a photo of ID or bank details before an interview, confirm the employer through its official website or a listed phone number — not a number from the posting itself — and treat any “immediate start, verification first” message as a red flag. For employers and job boards, it is equally simple: publish a clear statement of what you will never ask for upfront, verify postings before they go live, and give applicants a simple way to report a suspicious listing.
Affected applicants in this fictional case are being urged to place fraud alerts on their credit files, monitor bank statements, and report the postings to the job boards that carried them.
The job looked perfect. The application asked for everything. And the difference — one verification step, demanded before any human had spoken — was all it took.
Watching the perimeter — and what slips past it.
ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.

Ontario Exporters Wired Payments to Phantom Suppliers

Colonial Pipeline Wasn’t Just a Ransomware Story. It Was a Warning for Every Pipeline Operator.

Students Locked Out of Exams Days Before Finals

Reddit Thread Over ‘Inventory Drift’ Surges as Canadians Vent Over Retail Glitches

Are Canadian Companies Learning from Global Cyber Attacks? Insider Insights into the Secret Downfall of Canadian Businesses

Canadian Airline NorthSky Faces Cyberattack, Disrupting Online Services


-
 Business4 weeks ago
siberX Shipping extends telephone service across Pacific trading hours
-
 Cybersecurity2 weeks ago
Tourists Scanned. Strangers Collected.
-
 Business2 weeks ago
Winter Cargo Vanishes on Paper Trail
-
 Cybersecurity2 weeks ago
Winnipeg Distributor Loses Payment to Impostor Email
-
 Cybersecurity2 weeks ago
Regina Pharmacy Shut Out of Its Own Prescriptions
-
 Cybersecurity2 weeks ago
Nova Scotia Town Goes Dark Overnight
-
 Tech2 weeks ago
Cold Storage Warms While Dashboard Glows Green
-
 Tech1 week ago
Charlottetown Vaccines Hang on a Glitch