Business
Ghost Businesses Collected $2.3 Million in Loans

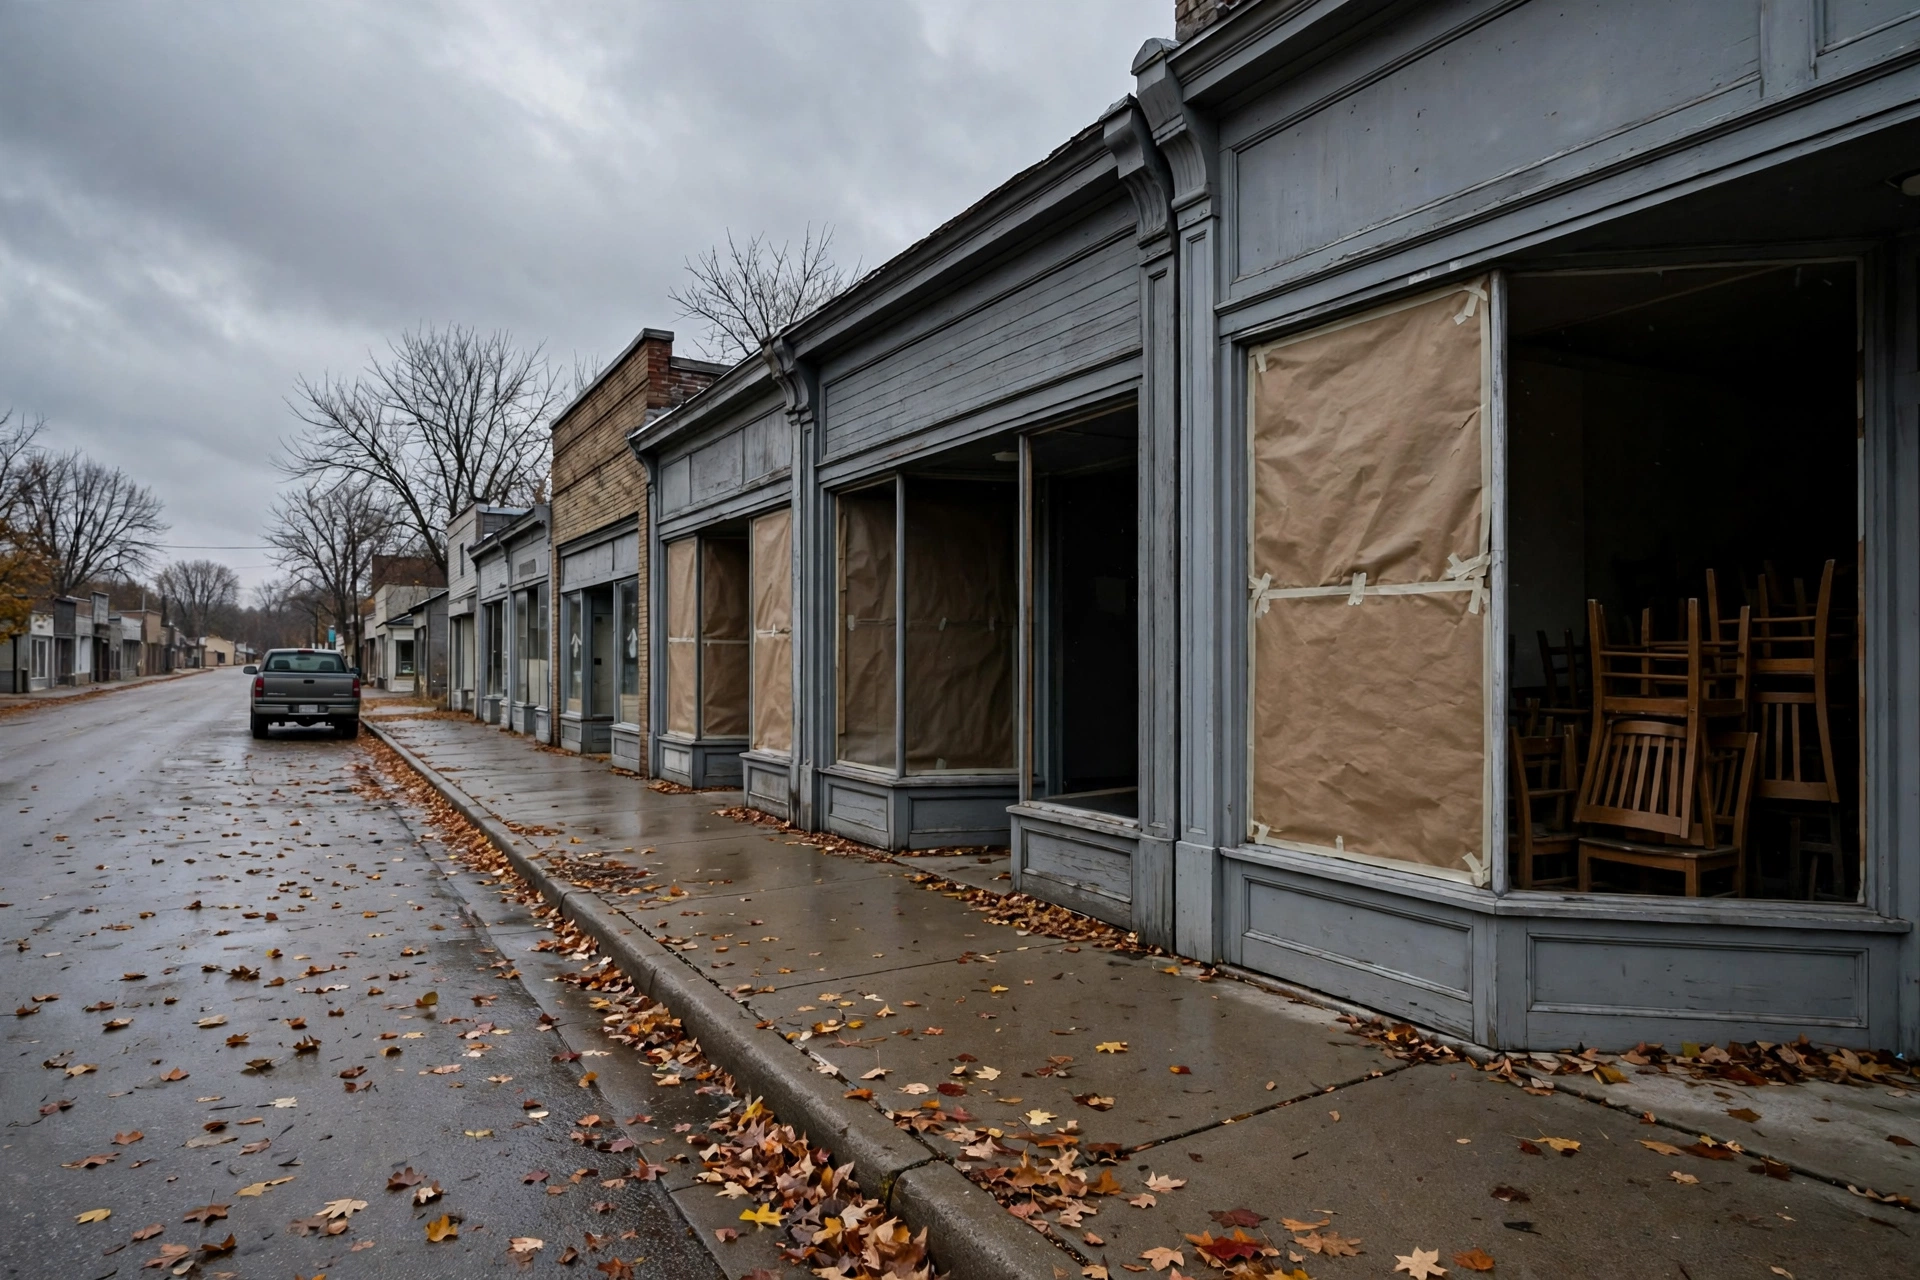
TARNWICK, Ont. — November 16, 2026 — The first loan was for $18,000, approved in nine minutes, for a bakery that has never baked a loaf. The forty-seventh was for $96,000, for a machine shop with no machines, no staff, and an address that turns out to be an empty lot behind the bus depot.
Tarnwick is a fictional Ontario town of about 21,000 people, and its Small Business Fund was supposed to be the town’s proudest idea: low-interest loans to help real shops, garages, and cafés survive a hard year. Between July and October, the fund approved 47 loans worth $2.3 million. This week, the town discovered that not one of those 47 businesses exists.
The money did not go to struggling shopkeepers. It went to storefronts that were never there, and the fund’s own paperwork said every one of them was real.
The fund’s checks looked solid on paper. Each application carried a business registration number, a phone number, a website, and two references. The fund’s staff verified the numbers against a registry, called the phones, and visited the websites. Every check came back clean — because the registry entries, the phones, the websites, and the references had all been set up by the same people applying for the money.
The one check that would have caught it was a visit to the address. The fund used to send someone to every applicant’s door before approving a loan. That practice was paused in the spring, when two staff members left and were never replaced, and the fund decided the paperwork checks were enough. Nobody told the town council the visits had stopped.
“We were approving loans faster than ever, and we took that as a sign the program was working,” said Elaine Marsh, the fictional fund’s director. “Forty-seven approvals in four months felt like forty-seven small businesses getting a chance. It was forty-seven empty rooms. The paperwork was perfect because the paperwork was the product. There was never a business behind it.”
The fund trusted documents that anyone could print. The documents trusted the fund right back.
Meanwhile, real businesses in Tarnwick were being turned away. Tom Beckett, who runs a fictional hardware store on Main Street, applied for $25,000 in August to replace a roof that leaks every time it rains. He was refused — the fund said his revenue history was too thin. “I have been open eleven years. I pay my taxes in this town, I hire kids from this town, and I got a no in three weeks,” Beckett said. “Somebody with a website and a phone number got a yes in nine minutes. I would like to know what my eleven years were worth.”
The town says the money was wired to accounts that were emptied within days, and it does not expect to recover most of it. The fund has frozen all new lending, and the town says it will not restart the program until every application is checked in person, every registration number is confirmed with the province directly, and no loan is approved on paperwork alone.
“These funds exist because a loan from a bank is too slow or too hard for a small shop,” said Dr. Helen Okafor, a fictional researcher who studies how small-business lending is abused. “So towns build a faster, friendlier process — and then they forget that the slow parts were the parts doing the checking. Speed is not a service if the money leaves town and never comes back.”
Tarnwick’s fund was built to move fast for real businesses. It moved fastest for the ones that were never there.
Across Canada, towns run loan funds, grant programs, and relief schemes on the same kind of trust: a form, a phone call, a website, and the belief that nobody would bother faking a small business for $18,000. In Tarnwick, somebody bothered 47 times — and the town’s real shopkeepers are the ones still waiting for help.
Lessons Learnt
- Never approve money on paperwork alone. Before any loan or grant is paid, someone from your organization should visit the address, meet the owner, and see the business operating. A visit is not bureaucracy — it is the one check that cannot be faked from a laptop.
- Ask your team what checks were quietly dropped. When staff leave or budgets tighten, verification steps get paused and nobody announces it. Leaders should ask, in plain terms: what did we stop checking, and when did we stop?
- Verify registrations with the source, not the applicant. A registration number on a form is a claim, not proof. Confirm it directly with the issuing authority, and treat a phone number or website supplied by the applicant as their own marketing, not evidence.
- Protect the real applicants first. Every dollar paid to a business that does not exist is a dollar a real shopkeeper cannot borrow. When a program moves fast, ask who is being left behind by that speed — and slow down for them.
Tarnwick’s town council meets Thursday to decide whether the fund continues at all. Beckett says he will be there, roof still leaking, application still open.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.




WRENFIELD, Ont. — November 13, 2026 — Four hundred and twelve people woke up on Friday expecting to be paid. None of them were. The money was in their employers’ accounts. The hours had been logged, the deductions calculated, the deposits scheduled. But the company that moves the money from one account to the other had gone dark overnight, and by the time anyone understood why, payday was already over.
Lakeshore Payroll Services is a fictional payroll firm in Wrenfield, a fictional Ontario town of about 14,000 people, that handles pay for roughly forty small businesses across the region — bakeries, diners, a hardware store, a landscaping crew, a daycare, and a dozen more. On Thursday evening, the firm’s computers locked up. The files that hold every client’s pay runs, tax deductions, and bank details were encrypted behind a ransom demand, and the staff could not open a single one.
More than four hundred workers went unpaid on a Friday — because the company that runs their payroll was locked out of its own files.
The firm says the trouble started with an email to its bookkeeping desk on Wednesday afternoon. It looked like a routine message from a fictional benefits provider, asking a bookkeeper to open an attached form. She did. The ransomware inside it spread through the office network in under an hour, and by Thursday morning the payroll system itself was locked. The firm says it did not pay the ransom, and no client data has been published. But the pay runs for Friday were inside the locked files, and there was no way to get them out in time.
“We had the money. We had the hours. We had everything except the file that puts the two together,” said Colin Barrett, the fictional firm’s owner. “I spent Friday morning on the phone with forty business owners, telling them their people would not be paid today, and I had no date I could give them. These are not big companies. Their staff live paycheque to paycheque. A missed Friday is a missed rent payment, a missed grocery run, a missed car payment — and it happened to all of them at once.”
Marta Kowalski, who runs a fictional bakery in Wrenfield, was one of the forty. She says she spent Friday afternoon writing paper cheques by hand for her nine staff, working from the hours she keeps in a notebook, while her own rent came due the same day. “I have run this bakery for eleven years and I have never missed a payday,” she said. “On Friday I was standing at my own counter, adding up hours on a calculator, because the company I pay to do this for me could not open its own computer. My staff were kind about it. They should not have had to be.”
The firm did not lose the money. It lost the list of who gets paid, and how much — and without that list, payday did not happen.
Payroll is the kind of service small businesses never think about until it stops. A bakery, a diner, or a daycare does not keep a payroll department; it pays a firm to handle the arithmetic, the deductions, and the deposits, and it trusts that the firm has its own backups and protections. When that firm goes down, the failure lands on forty employers at once — and on every one of their workers, at the same hour, on the same day.
“People picture a cyberattack on a business as a stolen credit card or a hacked website,” said Dr. Alan Reyes, a fictional small-business finance researcher who studies how small firms recover from attacks on their suppliers. “But the attacks that hurt ordinary people most are the ones that stop a service they never see. A payroll firm is a single point of failure for dozens of small employers. Lock its files on a Thursday night and four hundred people wake up unpaid on Friday — and none of them did anything wrong.”
In this fictional case, the firm says it rebuilt its payroll system from backups over the weekend and the missed pay runs went out on Monday, three days late. It says the bookkeeper’s email account has been rebuilt with a second login check, and the payroll files are now kept on a separate system from office email. It has not said how many workers were still waiting for their money by Monday, or whether any of the forty businesses have moved their payroll elsewhere.
The fictional businesses say they have since changed how they treat payday. Each one now keeps its own copy of staff hours and pay rates, updated every week, so a payroll failure does not leave them guessing. Several have agreed on a shared emergency plan: if the deposits do not land by Friday morning, the owners write paper cheques the same day, from their own records, instead of waiting for the firm to recover.
The defence is not a sharper eye for suspicious emails. It is never letting one locked file decide whether four hundred people get paid.
That advice applies well beyond one payroll firm. Across Canada, small businesses hand their most time-critical work — payroll, invoicing, scheduling — to a single outside provider, and rarely ask what happens if that provider goes down on the wrong day. A missed payday is not a data breach. It is a week of rent, groceries, and bills arriving on time while the money does not.
Lessons Learnt
- Ask your payroll provider how they would pay your people if their system went down. A good provider has a tested backup and a plain answer. If they cannot explain it, that is your answer.
- Keep your own copy of hours and pay rates, updated weekly. If the payroll firm cannot open its files, your own records let you pay people by cheque the same day instead of waiting.
- Hold a cash buffer for one payroll cycle. A missed payday becomes a crisis when there is nothing to bridge it. One cycle’s worth of payroll in reserve buys your staff time.
- Put payday in your incident plan. Decide now who writes the cheques, who tells the staff, and what you say to them. The first time you make that decision should not be on a Friday morning.
The fictional firm says the missed pay runs have now gone out, and the workers from Wrenfield’s small businesses have been paid. The money arrived three days late. The Friday it was supposed to arrive on is the part nobody gets back.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.
COPPERTON, Ont. — November 10, 2026 — The wire transfer was for $214,000, and it took eleven seconds to send. Elena Marsh, who owns a mid-sized food export business in Copperton, had paid the same supplier the same way for four years. The invoice looked right. The email address looked right. The only thing that had changed was the bank account number at the bottom — and by the time anyone noticed, the money was gone.
Marsh is one of at least a dozen Ontario exporters who wired payments to bank accounts controlled by criminals this autumn, after attackers posed as a long-time supplier and sent out new payment instructions. The supplier was real. The invoices were real. The bank accounts were not.
A dozen Ontario exporters paid real invoices into accounts that did not belong to their supplier — and the money is gone.
The scheme was patient. For weeks, the attackers watched the email traffic between the exporters and Prairie Malt & Grain Co., a fictional Manitoba supplier that ships grain and milling products across the country. They learned the order cycle, the invoice format, and the names of the people who approve payments. Then, just as the autumn shipping season peaked, they sent a short message from an address one letter off the supplier’s real one: new banking details, effective immediately, please update your records.
“There was no urgency in it, no threat, nothing that would make you stop and think,” Marsh said. “It read like the kind of administrative note you get three times a year. I forwarded it to our bookkeeper the same afternoon, and the next invoice went to the new account. It felt like routine.”
The real supplier only discovered the switch when it called about an overdue balance. By then, the exporters had wired nearly $900,000 to accounts the criminals controlled, and the money had already been moved on. The fictional exporters say their banks were able to freeze a small portion of the transfers. The rest is gone.
The invoice was genuine. The supplier was genuine. Only the destination had changed.
Business email compromise works because it asks for nothing unusual. No malware, no ransom note, no locked system — just a familiar invoice, a familiar sender, and one changed detail at the bottom of the page. Finance teams process hundreds of supplier payments a month, and a new bank account notice arrives looking like the most boring email of the day. That is exactly why it works.
“Attackers don’t break into the payment system. They break into the conversation around it,” said Marcus Hale, a fictional payments-fraud consultant who advises mid-sized Canadian exporters. “They wait until the relationship is routine, then they change one thing. A company that would question a strange invoice will pay a familiar one without a second look — and by the time the real supplier calls, the money has crossed three borders.”
In this fictional case, the attackers had been inside the email chain for more than a month before sending the new banking details, according to investigators. They timed the switch for the busiest weeks of the shipping season, when finance staff were processing invoices at volume and had the least time to check. None of the exporters had a rule requiring a phone call to confirm a change of bank details.
The fictional exporters say they have since changed how supplier payments work. No bank account change is accepted by email alone — it must be confirmed by a phone call to a number the company already has on file. Payment approvals above a set amount now need a second person to sign off. And any message about new banking details is treated as suspicious until proven otherwise.
The defence is not a sharper eye for fake invoices. It is never changing where money goes on the strength of an email alone.
That advice applies well beyond one shipping season. Across Canada, small and mid-sized businesses pay suppliers the same way every month — same invoices, same senders, same routine — and a single changed account number is all it takes to redirect a payment. The defence is not a cleverer spam filter. It is a habit of verifying every change of payment details out of band, by phone, before a single dollar moves.
For businesses, the checklist is short: never update a supplier’s bank details from an email alone — confirm it by calling a number you already have; require two people to approve any payment above a set threshold; and treat any message about new banking details as a fraud attempt until proven otherwise. For suppliers, it is equally simple: never send new bank details by email, publish a standing warning that payment details only change by phone, and call your customers the moment an invoice goes unpaid.
The fictional exporters say the fraudulent accounts have been reported, and the real Prairie Malt & Grain Co. continues to ship to its Ontario customers.
The invoices were never fake. The supplier was never fake. And the difference — one phone call, made before the money moved instead of after — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.
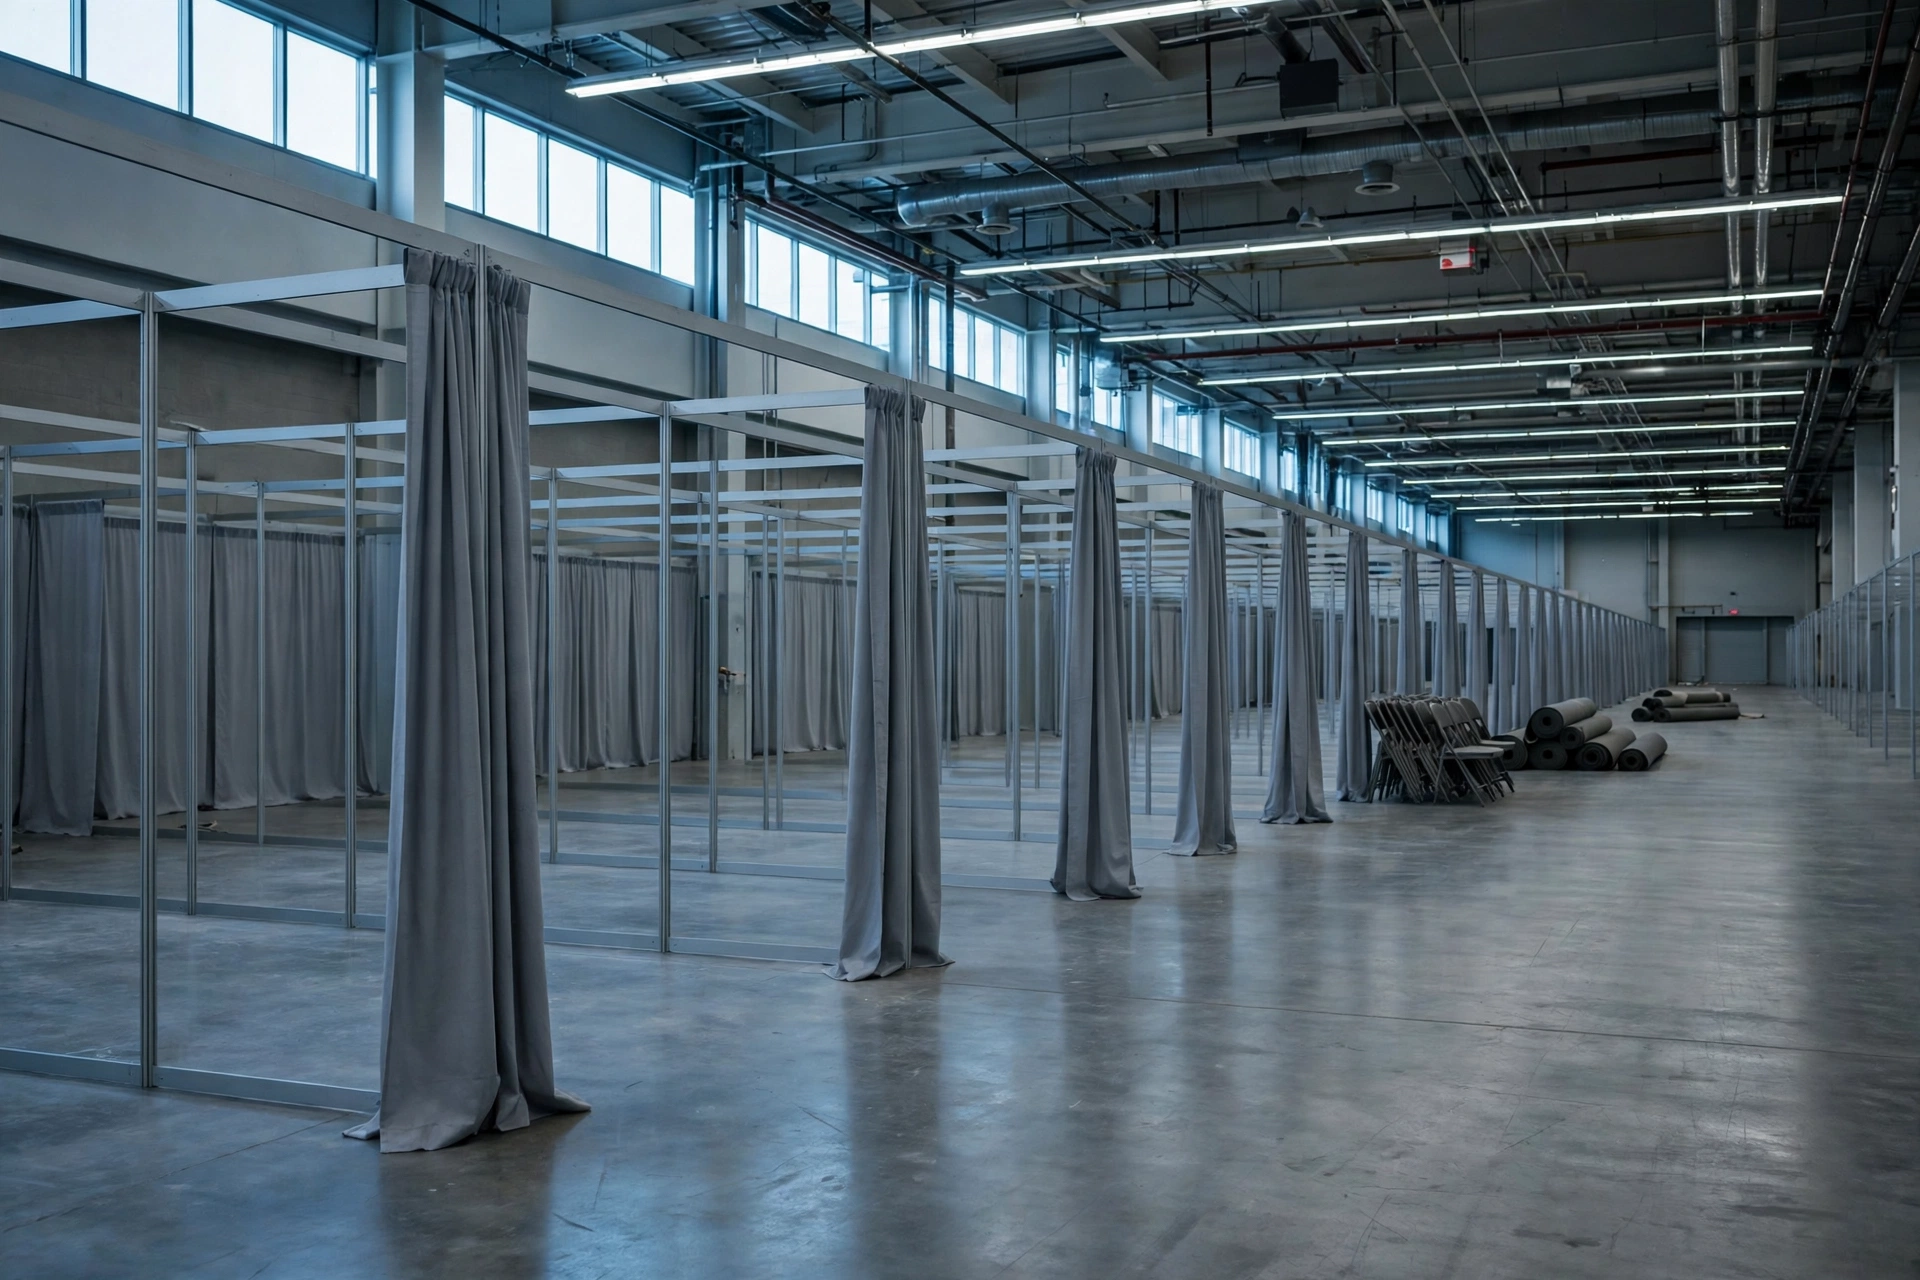
MAPLEFORD, Ont. — November 6, 2026 — “We had the banners printed before we realised there was no hall to hang them in,” said Rosa Almeida, owner of a fictional small packaging firm in Mapleford. “The floor plan had our booth number on it. The welcome email had our load-in time. Everything about it felt like a real trade show — except the trade show.”
Almeida was one of 41 small businesses that paid for booth space at a fictional event called the Northern Makers Expo, advertised as a two-day manufacturing and retail trade show at the Mapleford Convention Centre this month. Booths were priced between $2,400 and $6,800, depending on size and position on the floor plan. By the time one exhibitor rang the venue to confirm a forklift booking, the organisers had collected an estimated $180,000 — and the venue had no record of any expo at all.
The event had not been hacked or hijacked. It had simply been invented. A polished website carried the expo’s name, a speaker list, a floor plan, and a countdown clock. A fictional organiser, Harbourline Events Group, sent exhibitor packs, invoices, and a payment link for a “booth services” account. The site even listed a local hotel partner offering an exhibitor rate. The hotel had never heard of the expo. Neither had the venue, the listed speakers, or the trade association whose logo appeared on the site.
The expo never existed. The invoices were real enough to pay.
According to the fictional exhibitors who spoke to ODTN News, the scheme worked because every step of it looked like the normal run-up to a trade show. The exhibitor pack arrived on schedule. The floor plan was updated twice, with booths marked sold. A “final details” email went out a week before the supposed opening, asking exhibitors to confirm their power requirements and their arrival times. Several businesses ordered stock, printed banners, and booked hotel rooms before anyone thought to call the venue directly.
“We did what we always do,” said Almeida. “We checked the website, we checked the floor plan, we paid the invoice from the email the organiser sent us. Nobody checks whether the hall itself has the event in its book — you assume the organiser has done that part. That is the whole point of an organiser.”
A trade show is a trust business — and trust was the only thing on sale.
Small-business fraud advisors say fake expos are attractive precisely because exhibitors are used to paying upfront, months ahead, for something that does not exist yet. A booth is a promise: a patch of carpet, a table, and two days of foot traffic, sold long before the doors open. That gap between payment and delivery is exactly where a copycat event can live, collecting deposits from dozens of businesses before any of them arrives to find an empty hall.
“A real expo sells you a space that will exist,” said Mara Ellison, a fictional advisor who works with small manufacturers on payment fraud. “A fake one sells you the paperwork around the space — the floor plan, the invoice, the welcome pack. Every document feels like proof, and every document can be produced on a laptop in an afternoon. The only document that matters is the venue’s own booking, and almost nobody asks for it.”
In this fictional case, the money moved fast and quietly. Most exhibitors paid by e-transfer or wire to the “booth services” account named on the invoice, and several paid in full rather than in instalments, lured by an early-bird discount that expired the week the expo was announced. By the time the venue confirmed it had no booking, the account had been emptied and the expo’s phone line had stopped answering. The website stayed up for another day, still counting down to an opening that would never happen.
The fictional exhibitors say they have since changed how they book events. New shows are now checked against the venue’s own events calendar before any deposit is paid, and payments go only to accounts named on the venue’s own exhibitor information — never to an account that appears only on the organiser’s invoice. Several of the businesses have begun sharing the names of events they have verified, so a new show with no track record gets a phone call to the hall before it gets a deposit.
The fix, experts say, is a single phone call made before the money moves.
That advice applies well beyond one expo. Across Canada, small businesses pay deposits for trade shows, markets, and craft fairs months in advance, usually on the strength of a website and an invoice. The defence is not a cleverer booking platform. It is a habit of checking the venue’s own calendar before paying for a space in it.
For exhibitors, the checklist is short: confirm the event on the venue’s own website or by phone, pay only to an account the venue itself confirms, and be suspicious of an early-bird discount that pressures a full payment before the event has a track record. For venues, it is equally simple: publish a public events calendar, answer exhibitor verification calls quickly, and flag any event using the venue’s name that is not in the book.
The fictional exhibitors say the expo’s website has been reported for removal, and the payments have been reported to their banks.
The booths were sold. The hall was never booked. And the difference — one call to the venue, made before the deposit — was all it took.
Watching the perimeter — and what slips past it.
ODTN News note: ODTN.News is a fictional news platform set within the Operation: Defend the North universe. All names, organizations, quotes, and events in this article are entirely fictitious. Any resemblance to real people, companies, or incidents is purely coincidental. The cybersecurity challenges it represents are very real.

Nine Hundred Voters Vanished From the Rolls

Smart Locks Left Hundreds Outside in the Cold

Ghost Businesses Collected $2.3 Million in Loans

Reddit Thread Over ‘Inventory Drift’ Surges as Canadians Vent Over Retail Glitches

Are Canadian Companies Learning from Global Cyber Attacks? Insider Insights into the Secret Downfall of Canadian Businesses

Canadian Airline NorthSky Faces Cyberattack, Disrupting Online Services


-
 Cybersecurity3 weeks ago
Tourists Scanned. Strangers Collected.
-
 Cybersecurity3 weeks ago
Sudbury Boss’s Voice Calls From Another Phone
-
 Tech2 weeks ago
Smart Doorbells Streamed Porches to Strangers
-
 Cybersecurity3 weeks ago
Winnipeg Distributor Loses Payment to Impostor Email
-
 Cybersecurity3 weeks ago
Regina Pharmacy Shut Out of Its Own Prescriptions
-
 Cybersecurity3 weeks ago
Nova Scotia Town Goes Dark Overnight
-
 Business3 weeks ago
Winter Cargo Vanishes on Paper Trail
-
 Tech2 weeks ago
Kingston Drivers Charge Cars, Drain Accounts